Framework mapping
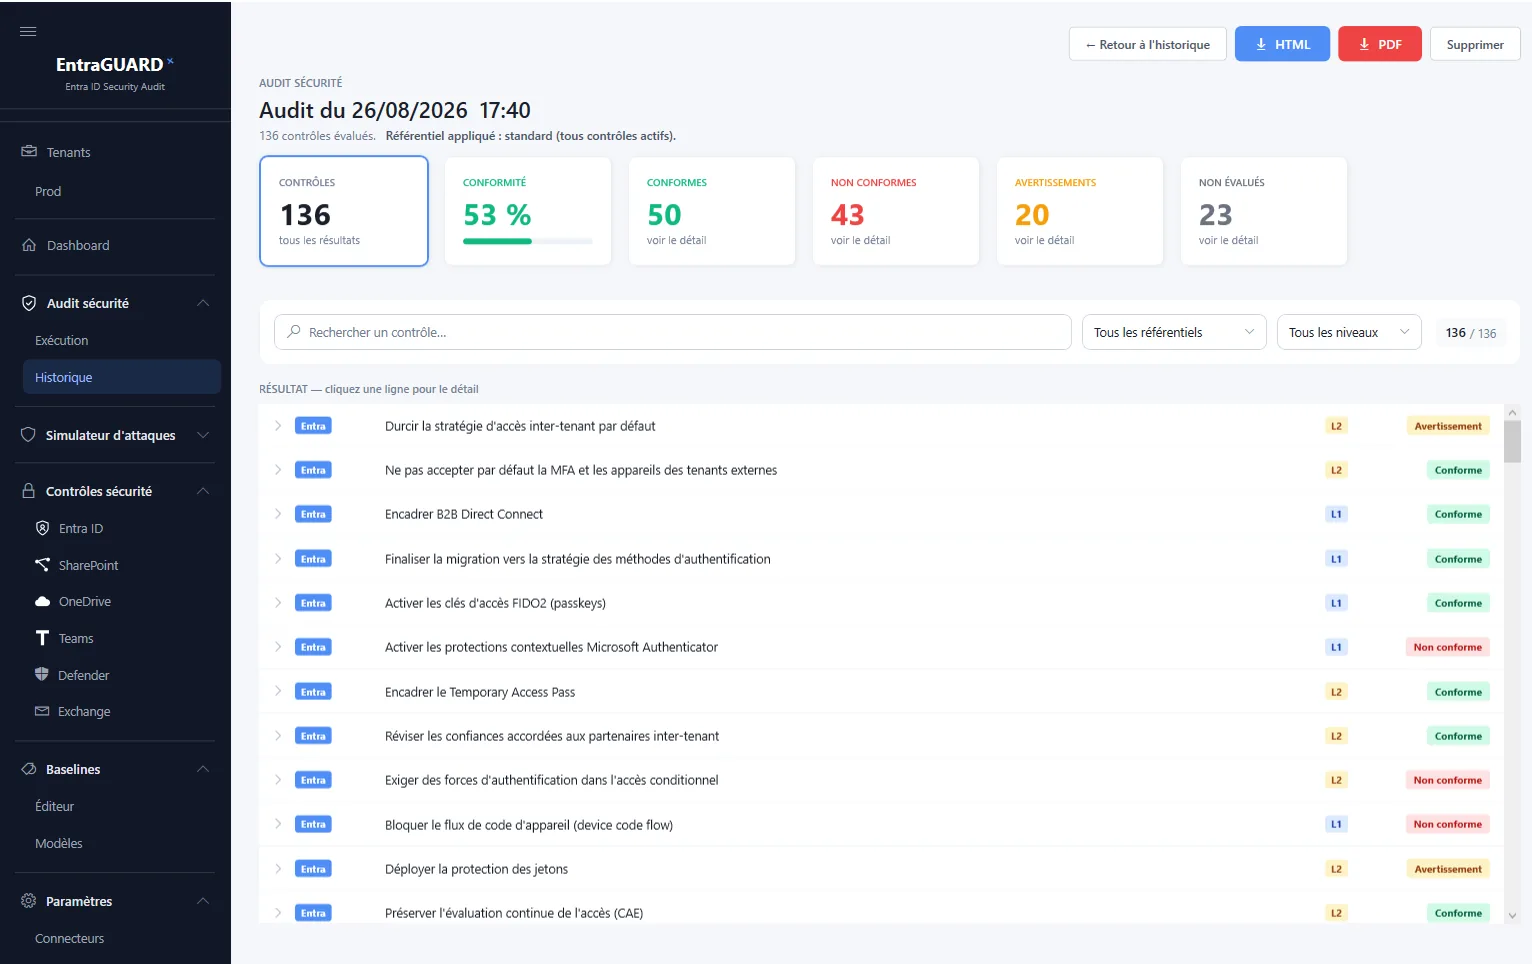
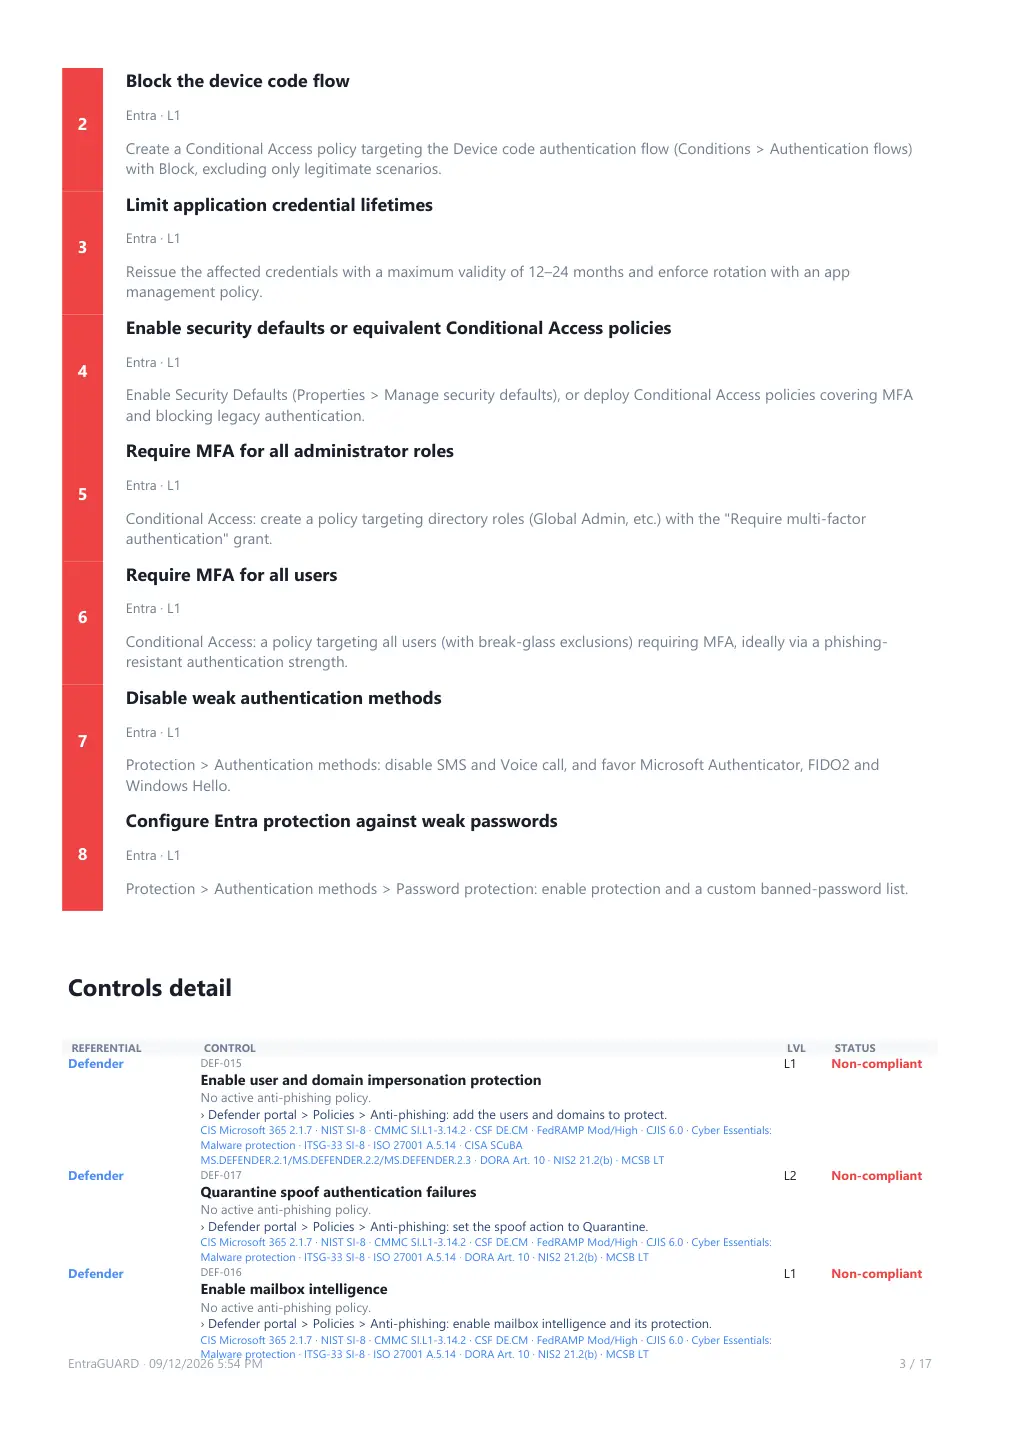
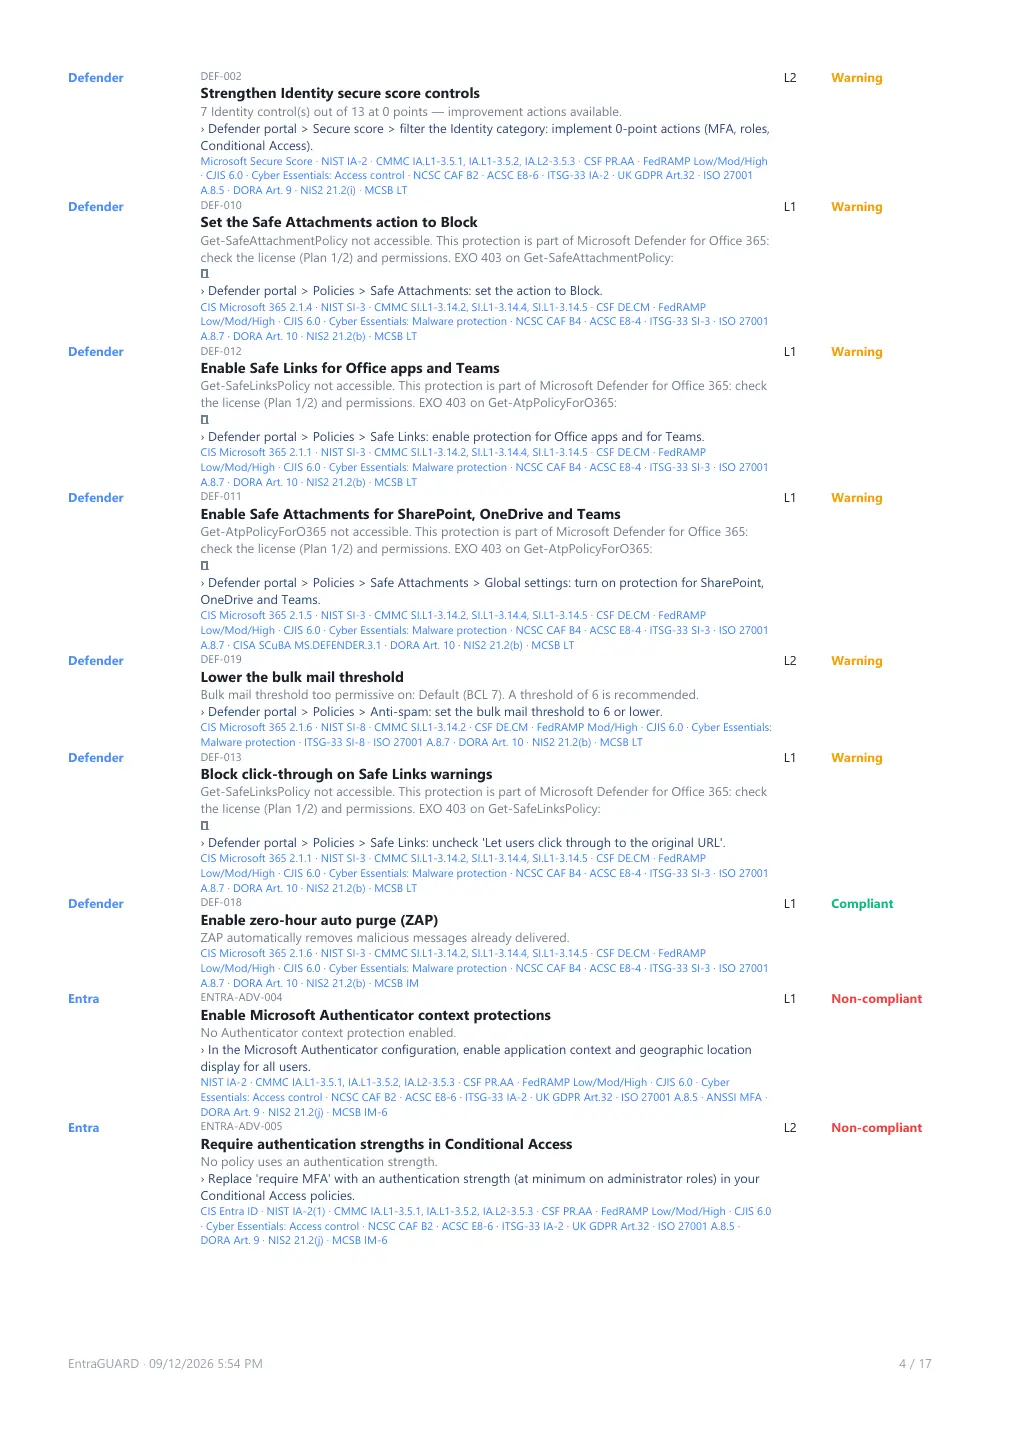
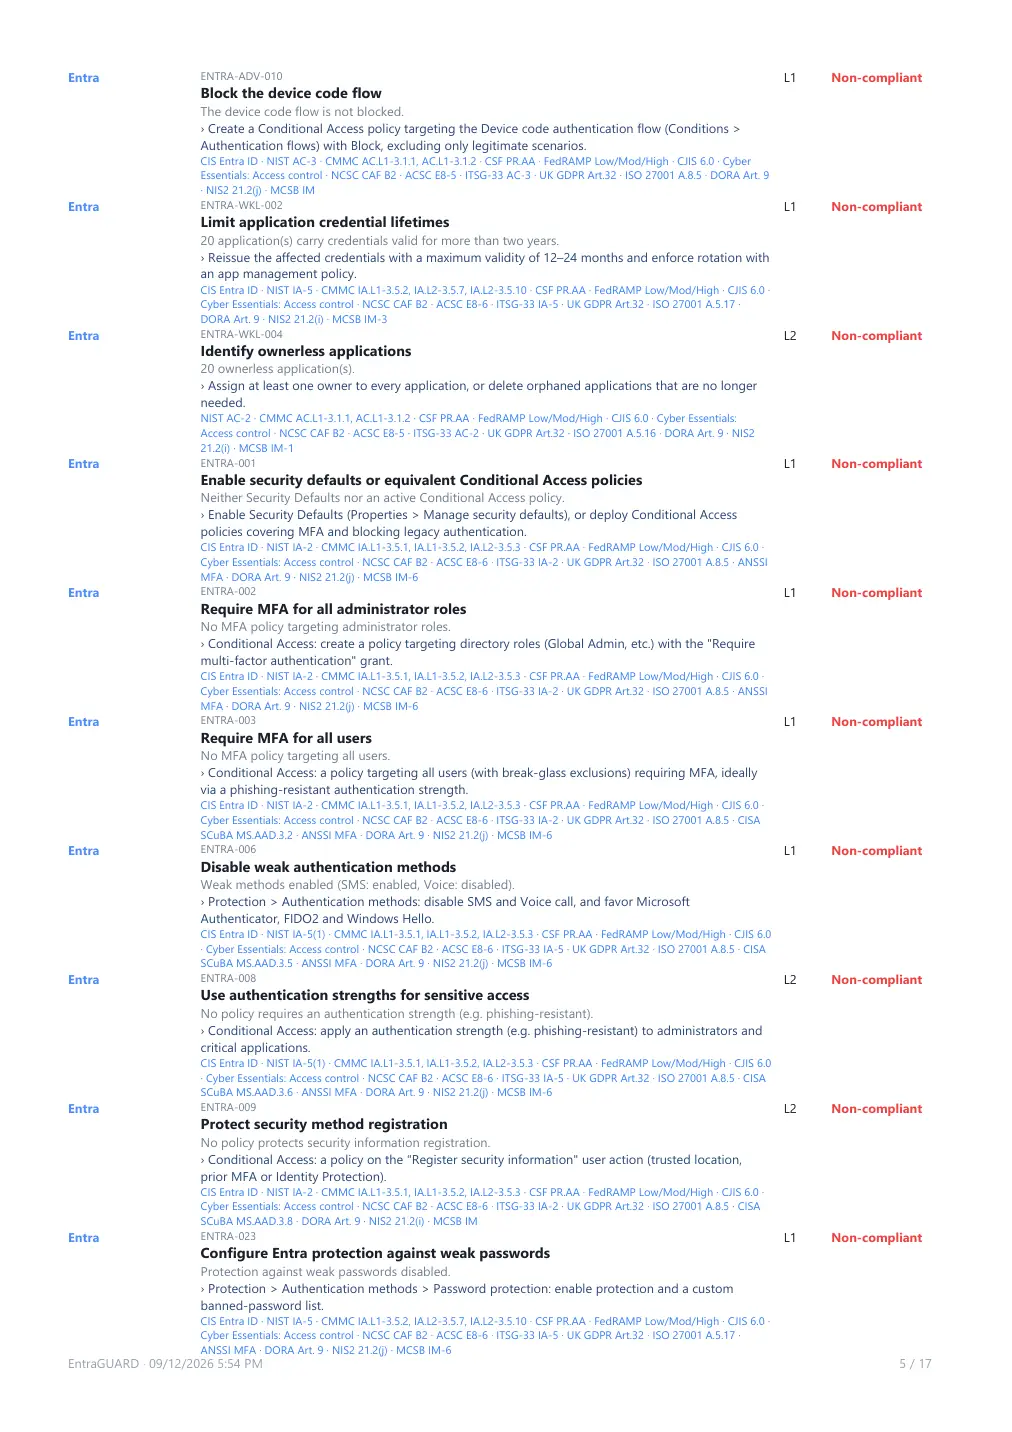
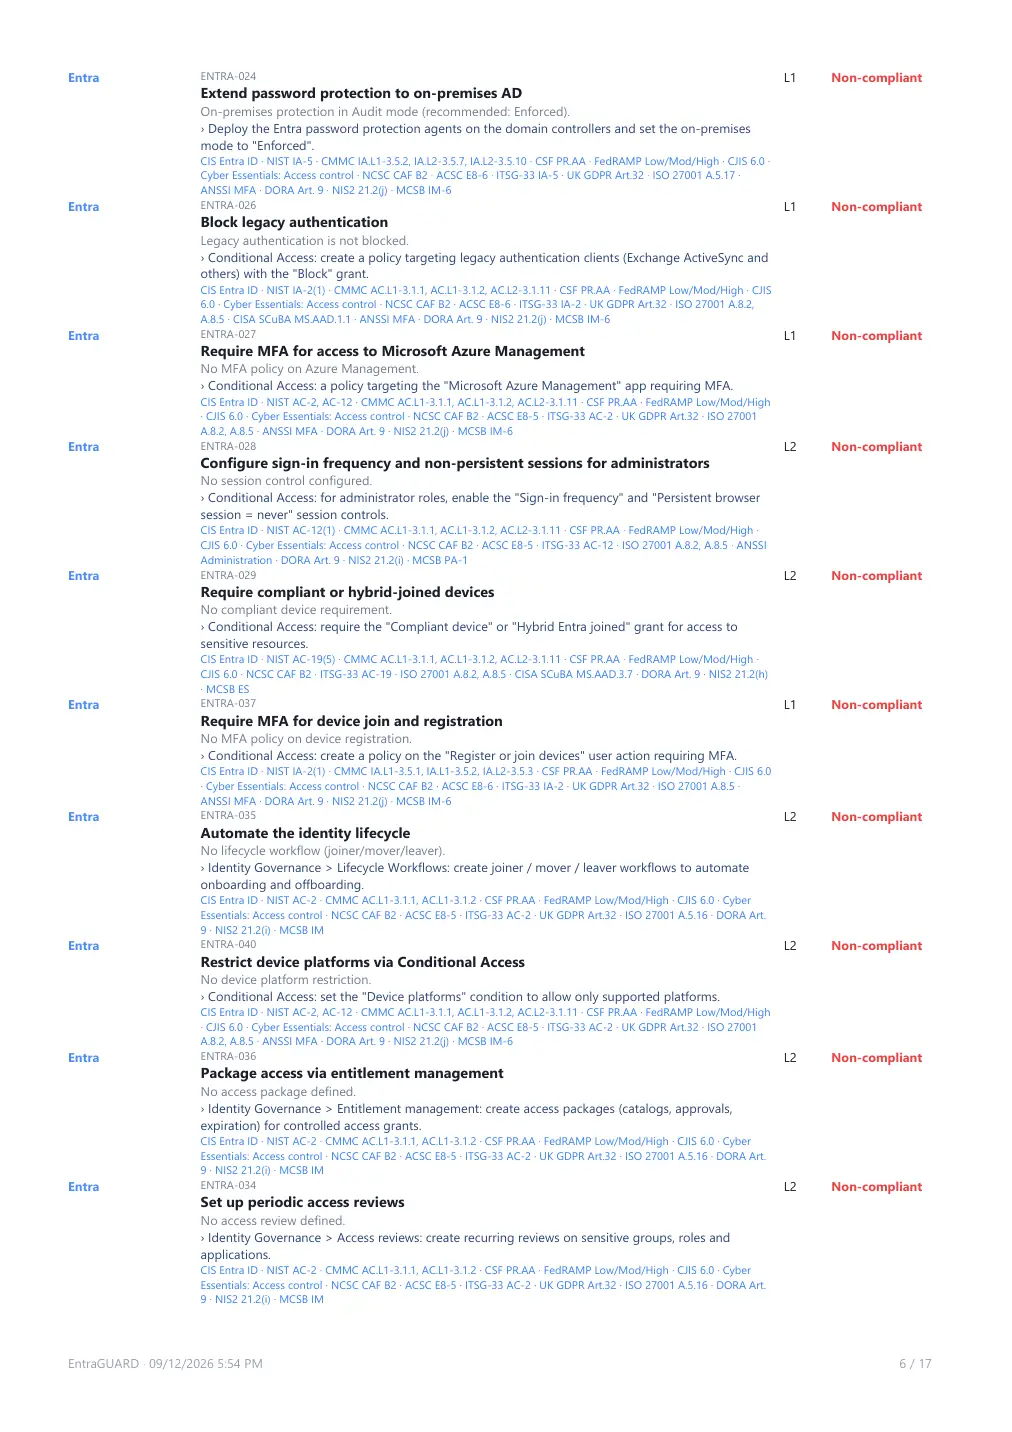
Every control cites its source.
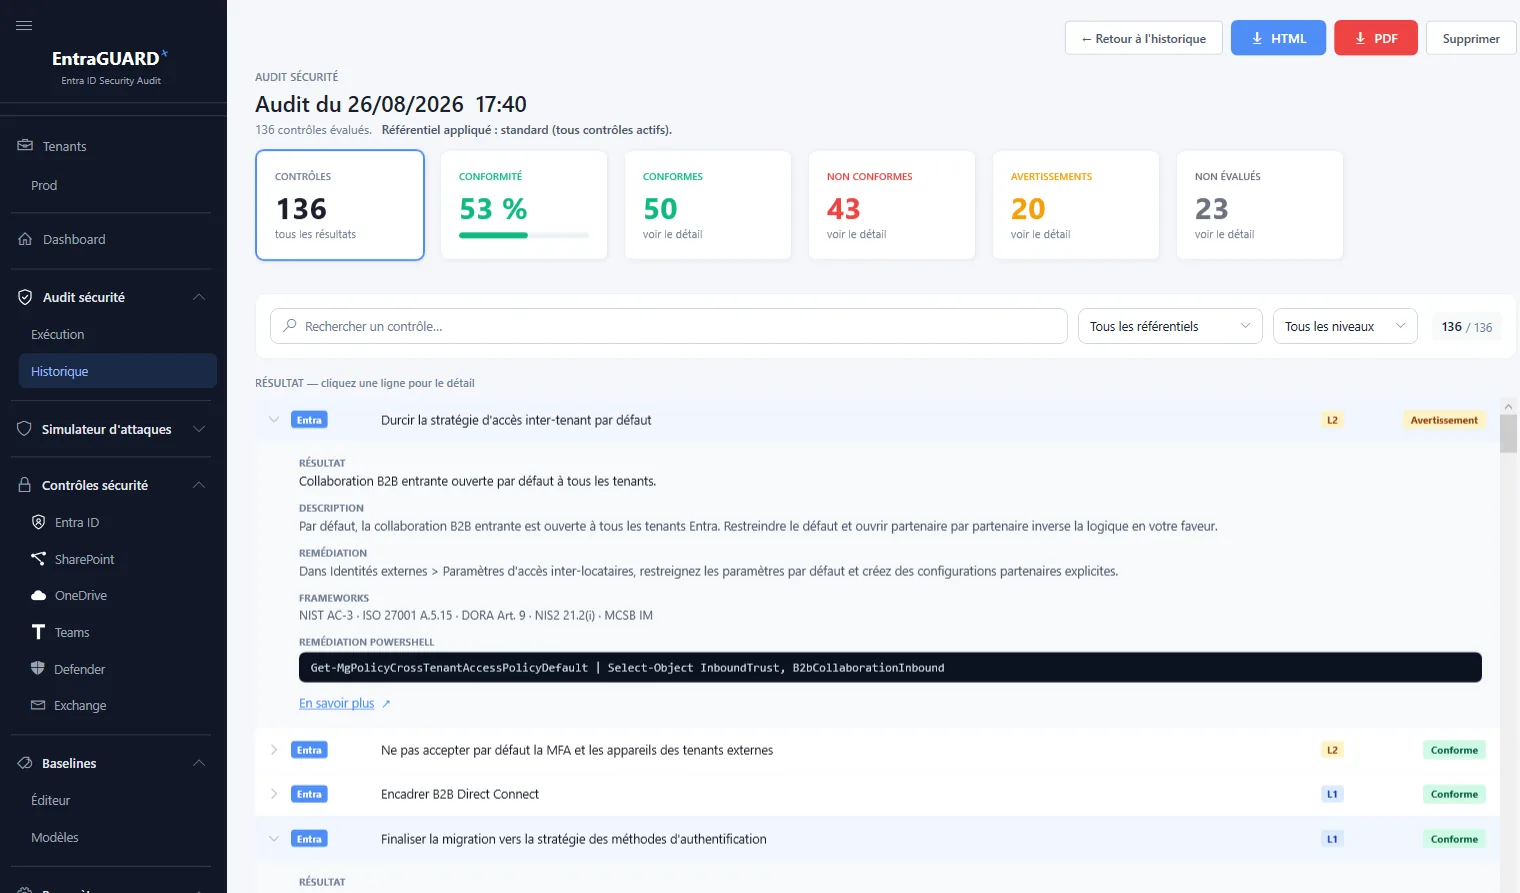
Auditors don't accept findings without a reference. Each control carries the exact
requirement it answers in every framework that covers it — nineteen of them, from the CIS
recommendation number and the NIST 800-53 enhancement to the CMMC practice, the ISO 27001
annex clause and the NIS2 article. One run, every reference already written.
NIST SP 800-53 Rev. 5
AC, IA, SC, SI and AU families, down to the enhancement where it applies — IA-2(1), AC-12(1), AC-17(1), AC-19(5)
NIST CSF 2.0
The subcategory each control answers: PR.AA for identity, PR.IR for boundaries, DE.CM for detection, PR.PS for platform
CMMC 2.0 / SP 800-171
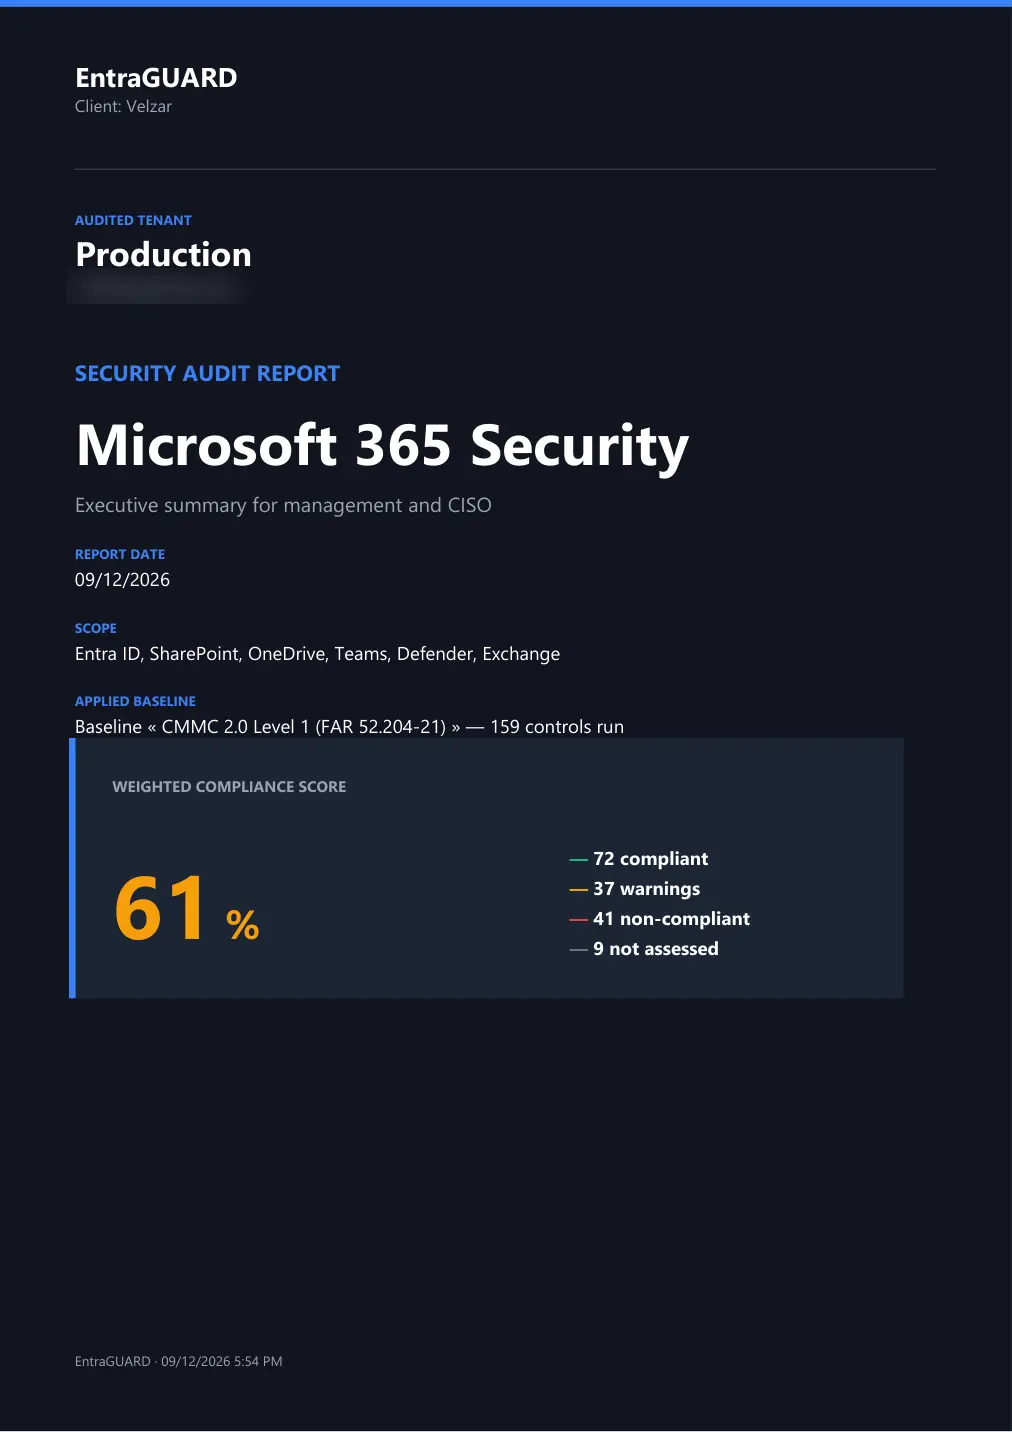
Practice identifiers for both levels — AC.L1-3.1.1, IA.L1-3.5.2, IA.L2-3.5.3, SI.L1-3.14.2 — via the 800-171 Rev. 2 crosswalk
FedRAMP
The Low, Moderate and High baselines each control belongs to, for cloud services carrying federal data
CJIS Security Policy 6.0
Now aligned on 800-53 identifiers, so criminal-justice agencies read the same control set
ISO/IEC 27001:2022
Annex A.5 organizational and A.8 technological clauses — A.5.17, A.8.2, A.8.5, A.8.23
NIS2 — EU 2022/2555
Article 21.2 risk-management measures: (b) incident handling, (h) cryptography, (i) access control, (j) MFA
DORA — EU 2022/2554
ICT protection and prevention (Art. 9) and detection (Art. 10) for financial entities
Microsoft Cloud Security Benchmark
IM, PA, DP, LT and ES families — Microsoft's own cross-cloud baseline
ITSG-33 (Canada)
The Canadian control catalog, mapped through its 800-53 lineage: AC, IA, SC, SI
Cyber Essentials (UK)
The five technical controls: access control, malware protection, firewalls, security update management
NCSC CAF
Objective B2 identity and access management and B4 system security, for UK operators of essential services
ACSC Essential Eight
Mitigation strategies E8-2 patching, E8-4 macro and content protection, E8-5 admin privileges, E8-6 MFA
CIS Benchmarks
CIS Entra ID and CIS Microsoft 365, with the numbered recommendation — 1.1.5, 2.1.7, 6.2.3 — the source of the controls
UK GDPR Art. 32
Security of processing, for the controls that protect personal data in the tenant
CISA SCuBA
The federal Microsoft 365 baseline, natively implemented: MS.AAD, MS.EXO, MS.DEFENDER and MS.TEAMS identifiers
ANSSI
Recommendations grouped as the agency publishes them: MFA, administration, hybrid identity, email, logging
Microsoft Secure Score
The improvement actions Microsoft itself scores, so the two views can be reconciled
MITRE ATT&CK
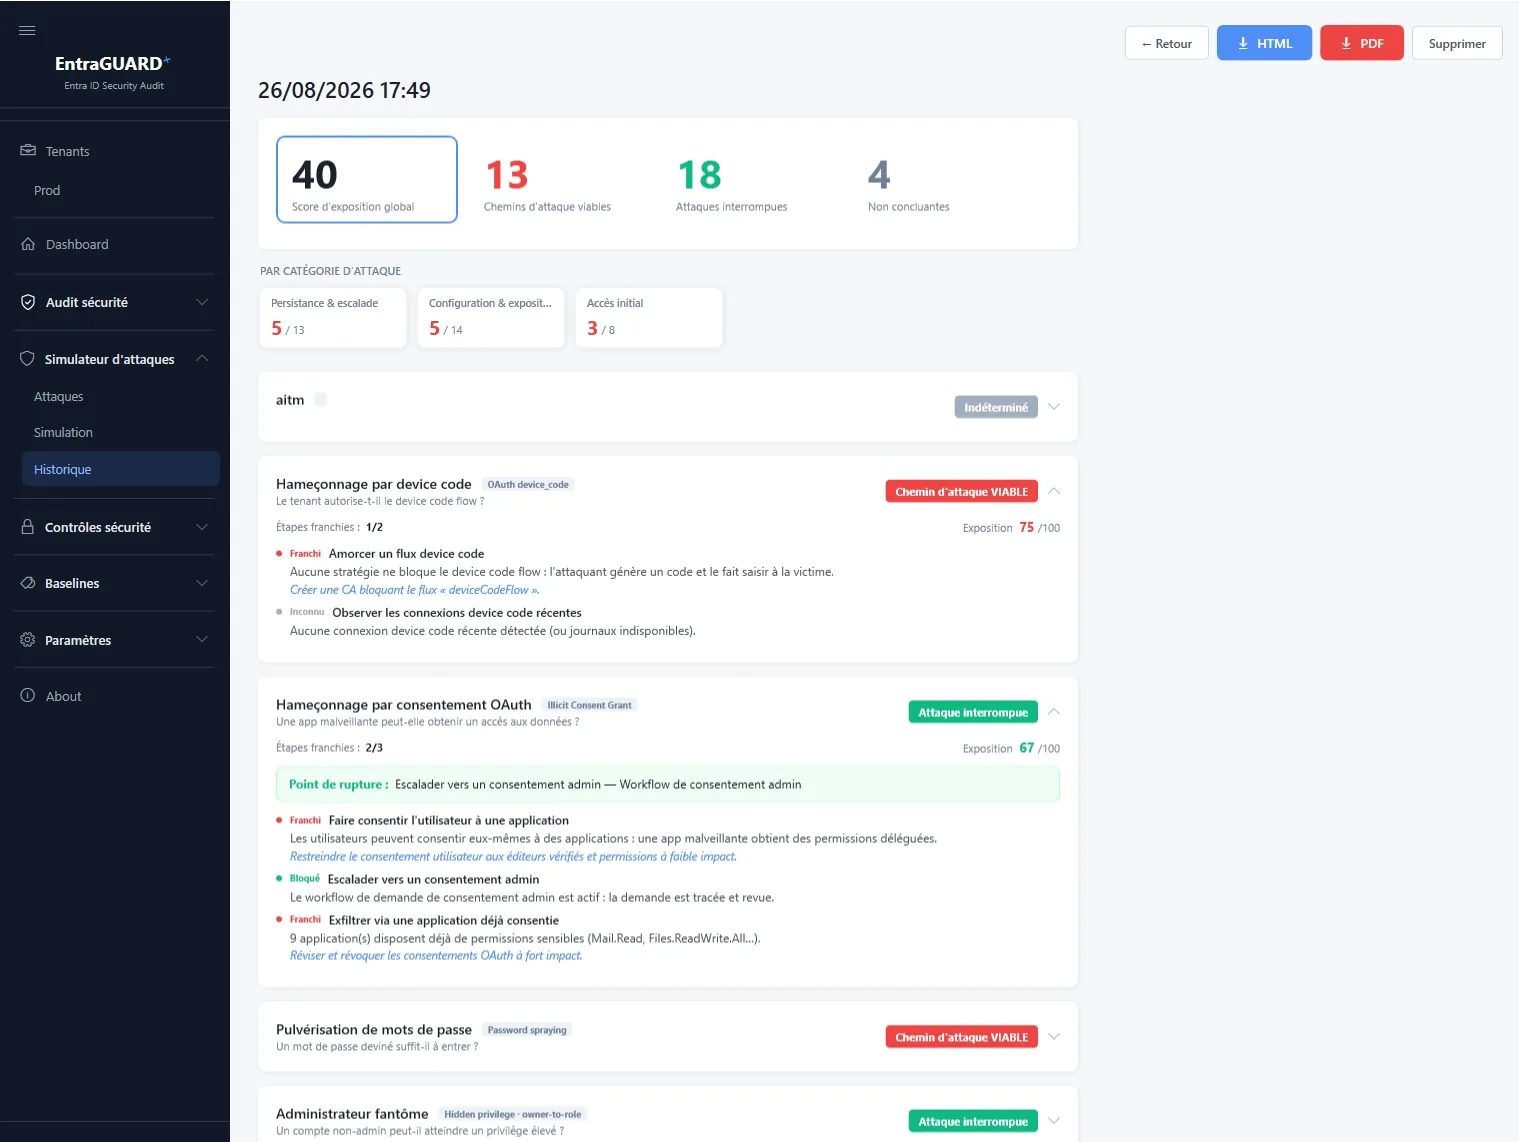
Techniques on the federation controls — T1484.002 domain trust modification, Golden SAML territory