Microsoft 365 & Entra ID security audit software

V2Attack simulator included

It runs on its own.That doesn't mean you're on your own.

Coverage

318 controls. Every one of them runs.

No placeholders, no planned entries padding a marketing number. Each control in the catalog is backed by a live check against the Microsoft API — now across eight services including Intune device management — and returns a verdict with the objects it found.

132

Microsoft Entra ID

MFA, conditional access, PIM, privileged roles, guests, identity protection, federation, device compliance

68

Exchange Online

Mail flow rules, connectors, legacy protocols, forwarding, DLP, DKIM, delegation, litigation hold

28

Microsoft Teams

External access, meeting policy, guest permissions, recording, app governance

23

Microsoft Intune

Device compliance, configuration profiles, update rings, BitLocker, ASR, EDR, app protection

22

Microsoft Defender

Safe Links, Safe Attachments, anti-phishing, impersonation, ZAP, quarantine

19

SharePoint

External sharing, anonymous links, unmanaged devices, custom script, site creation

17

Microsoft Purview

DLP coverage by workload, sensitivity labels, retention, insider risk, audit retention

9

OneDrive

Sync restrictions, retention after offboarding, file types, device policy

Each control carries a level — L1 for foundational, L2 for hardening — and the score weights them accordingly. A failed L1 costs three times a failed L2, because it should.

Beyond compliance, EntraGUARD also simulates attacks — 35 read-only scenarios in three phases that replay an intruder’s path and score your real exposure. See attack simulation →

Framework mapping

Every control cites its source.

Auditors don't accept findings without a reference. Each control carries the exact requirement it answers in every framework that covers it — nineteen of them, from the CIS recommendation number and the NIST 800-53 enhancement to the CMMC practice, the ISO 27001 annex clause and the NIS2 article. One run, every reference already written.

NIST SP 800-53 Rev. 5

AC, IA, SC, SI and AU families, down to the enhancement where it applies — IA-2(1), AC-12(1), AC-17(1), AC-19(5)

NIST CSF 2.0

The subcategory each control answers: PR.AA for identity, PR.IR for boundaries, DE.CM for detection, PR.PS for platform

CMMC 2.0 / SP 800-171

Practice identifiers for both levels — AC.L1-3.1.1, IA.L1-3.5.2, IA.L2-3.5.3, SI.L1-3.14.2 — via the 800-171 Rev. 2 crosswalk

FedRAMP

The Low, Moderate and High baselines each control belongs to, for cloud services carrying federal data

CJIS Security Policy 6.0

Now aligned on 800-53 identifiers, so criminal-justice agencies read the same control set

ISO/IEC 27001:2022

Annex A.5 organizational and A.8 technological clauses — A.5.17, A.8.2, A.8.5, A.8.23

NIS2 — EU 2022/2555

Article 21.2 risk-management measures: (b) incident handling, (h) cryptography, (i) access control, (j) MFA

DORA — EU 2022/2554

ICT protection and prevention (Art. 9) and detection (Art. 10) for financial entities

Microsoft Cloud Security Benchmark

IM, PA, DP, LT and ES families — Microsoft's own cross-cloud baseline

ITSG-33 (Canada)

The Canadian control catalog, mapped through its 800-53 lineage: AC, IA, SC, SI

Cyber Essentials (UK)

The five technical controls: access control, malware protection, firewalls, security update management

NCSC CAF

Objective B2 identity and access management and B4 system security, for UK operators of essential services

ACSC Essential Eight

Mitigation strategies E8-2 patching, E8-4 macro and content protection, E8-5 admin privileges, E8-6 MFA

CIS Benchmarks

CIS Entra ID and CIS Microsoft 365, with the numbered recommendation — 1.1.5, 2.1.7, 6.2.3 — the source of the controls

UK GDPR Art. 32

Security of processing, for the controls that protect personal data in the tenant

CISA SCuBA

The federal Microsoft 365 baseline, natively implemented: MS.AAD, MS.EXO, MS.DEFENDER and MS.TEAMS identifiers

ANSSI

Recommendations grouped as the agency publishes them: MFA, administration, hybrid identity, email, logging

Microsoft Secure Score

The improvement actions Microsoft itself scores, so the two views can be reconciled

MITRE ATT&CK

Techniques on the federation controls — T1484.002 domain trust modification, Golden SAML territory
Dashboard

Your security posture on one screen.

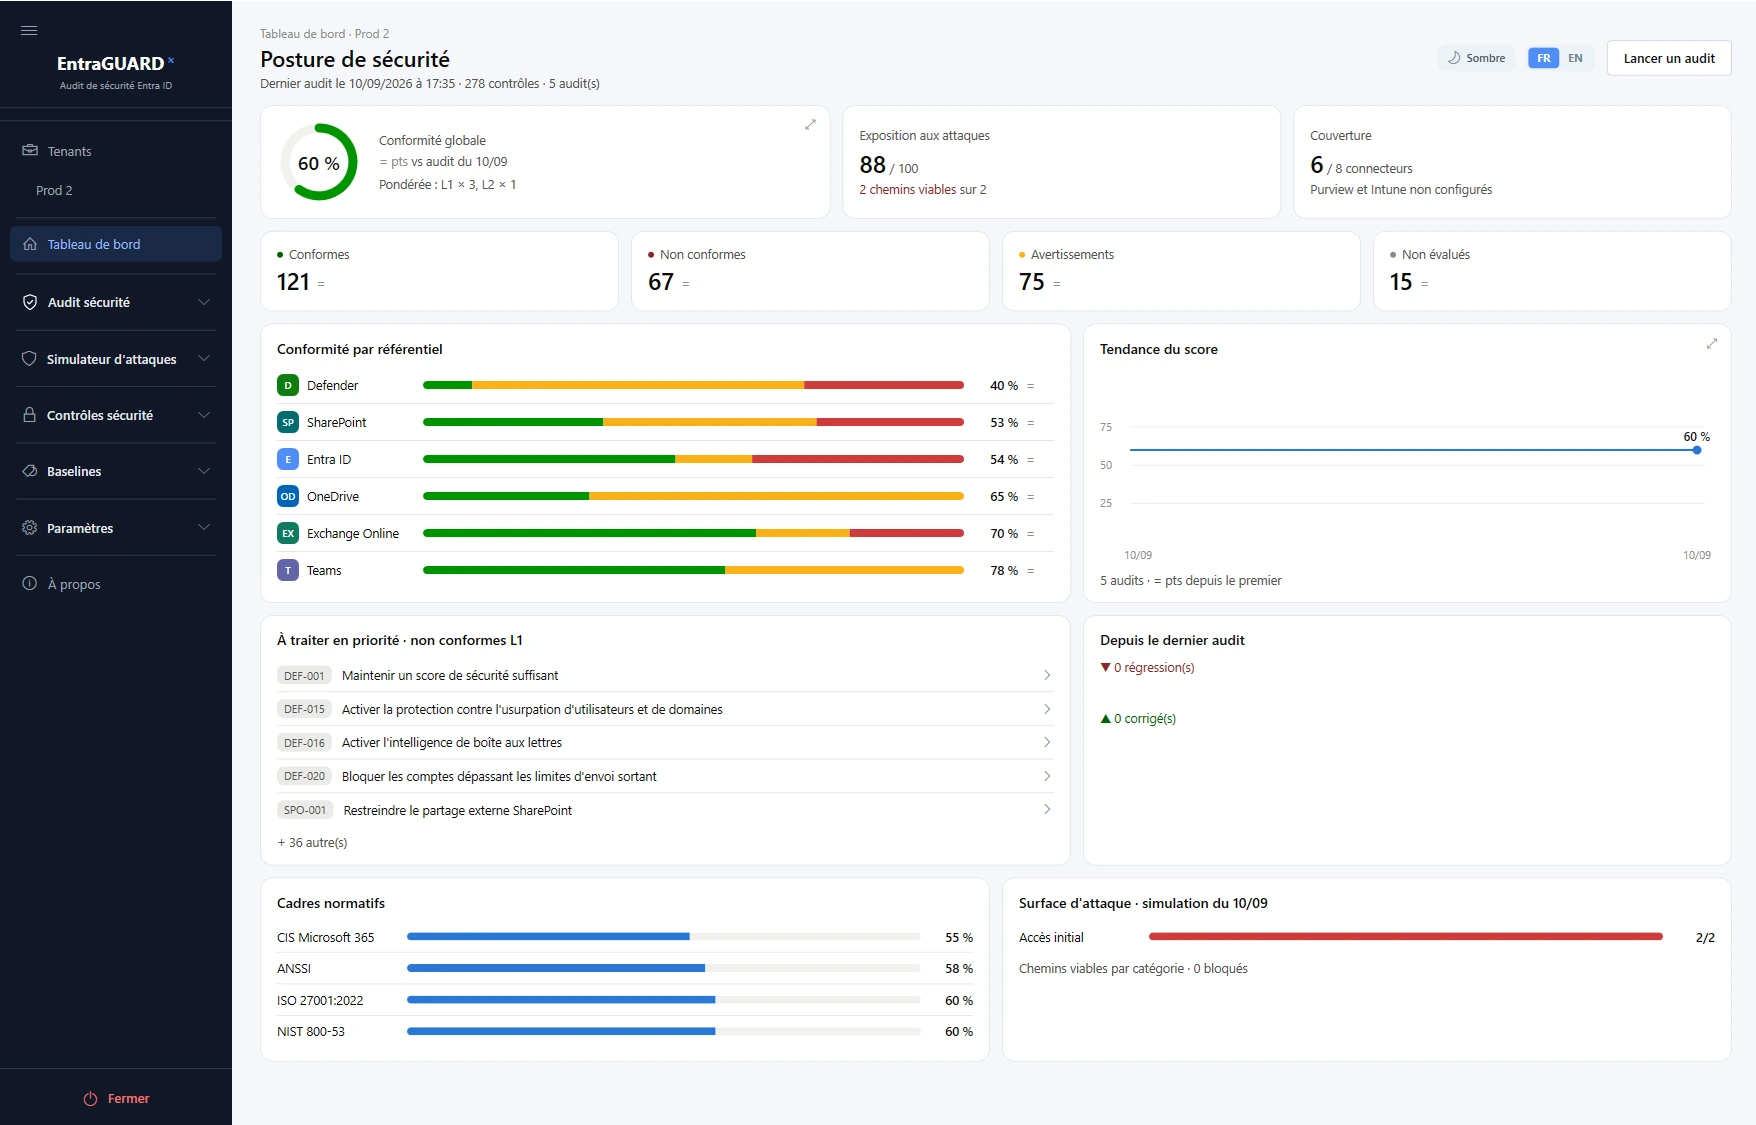
The dashboard opens on the last audit: weighted overall compliance, attack exposure and connector coverage, then compliance by service and by framework, the score trend, the L1 failures to fix first and what changed since the previous audit.

EntraGUARD dashboard: 60% weighted overall compliance, attack exposure 88/100, 6 of 8 connectors, compliant, non-compliant, warning and not-assessed counts, compliance by service and by framework, score trend, priority L1 failures and the attack surface from the last simulation

Weighted, not averaged

A failed L1 control weighs three times a failed L2 (L1 × 3, L2 × 1), so the 60 % shown here measures risk rather than a head count.

Running an audit

Real-time audit

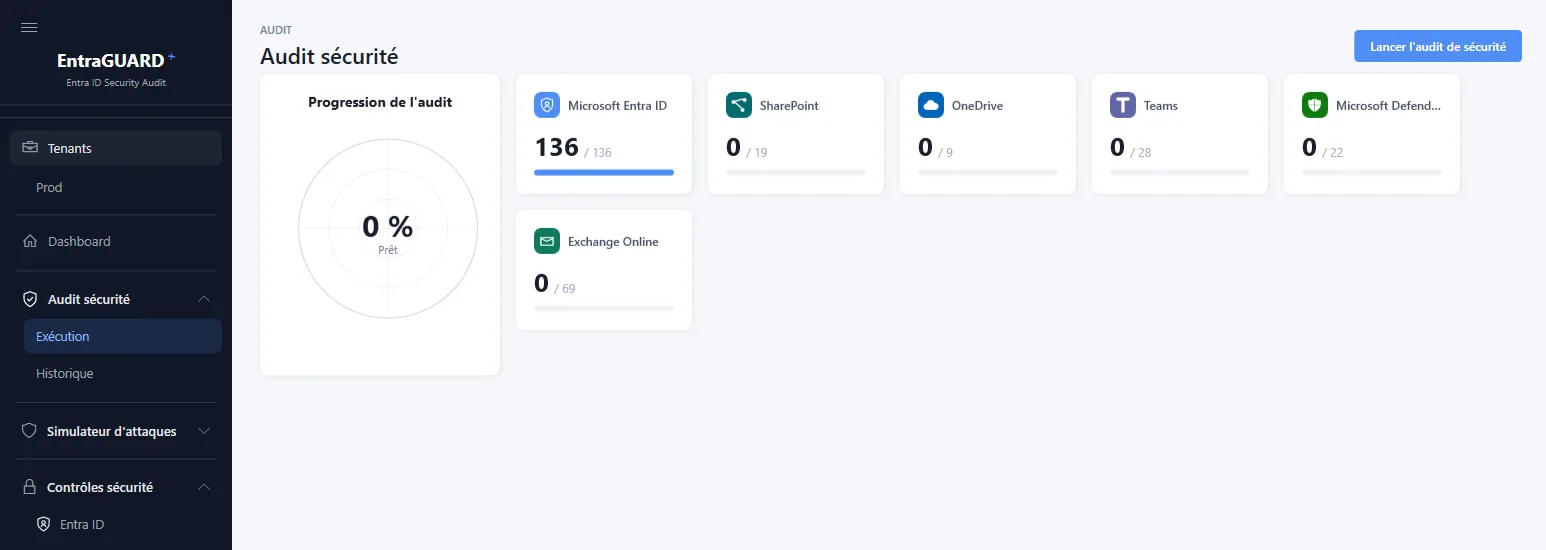
The scope is already decided by the baseline, so starting an audit is a single button. What follows is not a progress bar you leave running over lunch: the controls in scope are evaluated live across the selected services, with each finding appearing the moment it is produced.

Audit in progress: overall percentage, per-service counters and controls being analysed with their status

You watch it work

A counter per service and one overall — 81 / 194 here, on a run scoped to 194 controls — with the controls streaming past as they are evaluated. Each row carries its service, its level and its verdict, and a finding that needs explaining gets its sentence immediately: "7 service principals hold a directory role: these identities escape MFA and PIM, their justification must be documented." Nothing is buffered until the end.

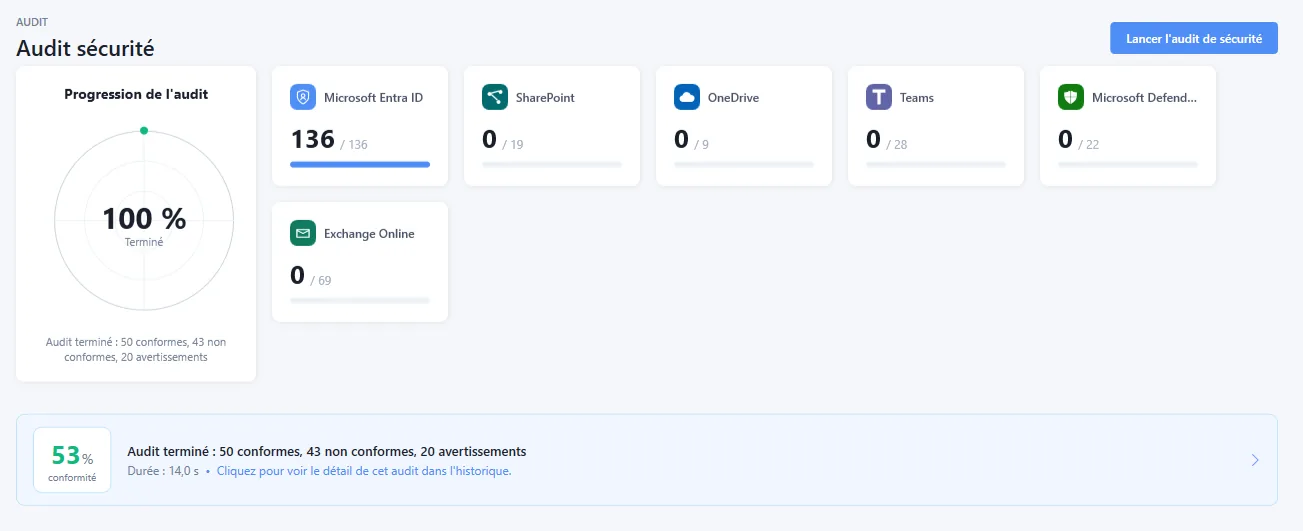
Completed audit showing 100% done, compliance score, compliant, non-compliant and warning counts, and duration

And it tells you how long it took

Done, on that same 194-control run: 51 % compliance, 64 compliant, 48 non-compliant, 82 warnings — in 16.1 seconds. The header keeps controls enabled out of 318 in view throughout, so a partial run can never be mistaken for a full one, and one click goes straight to the detail.

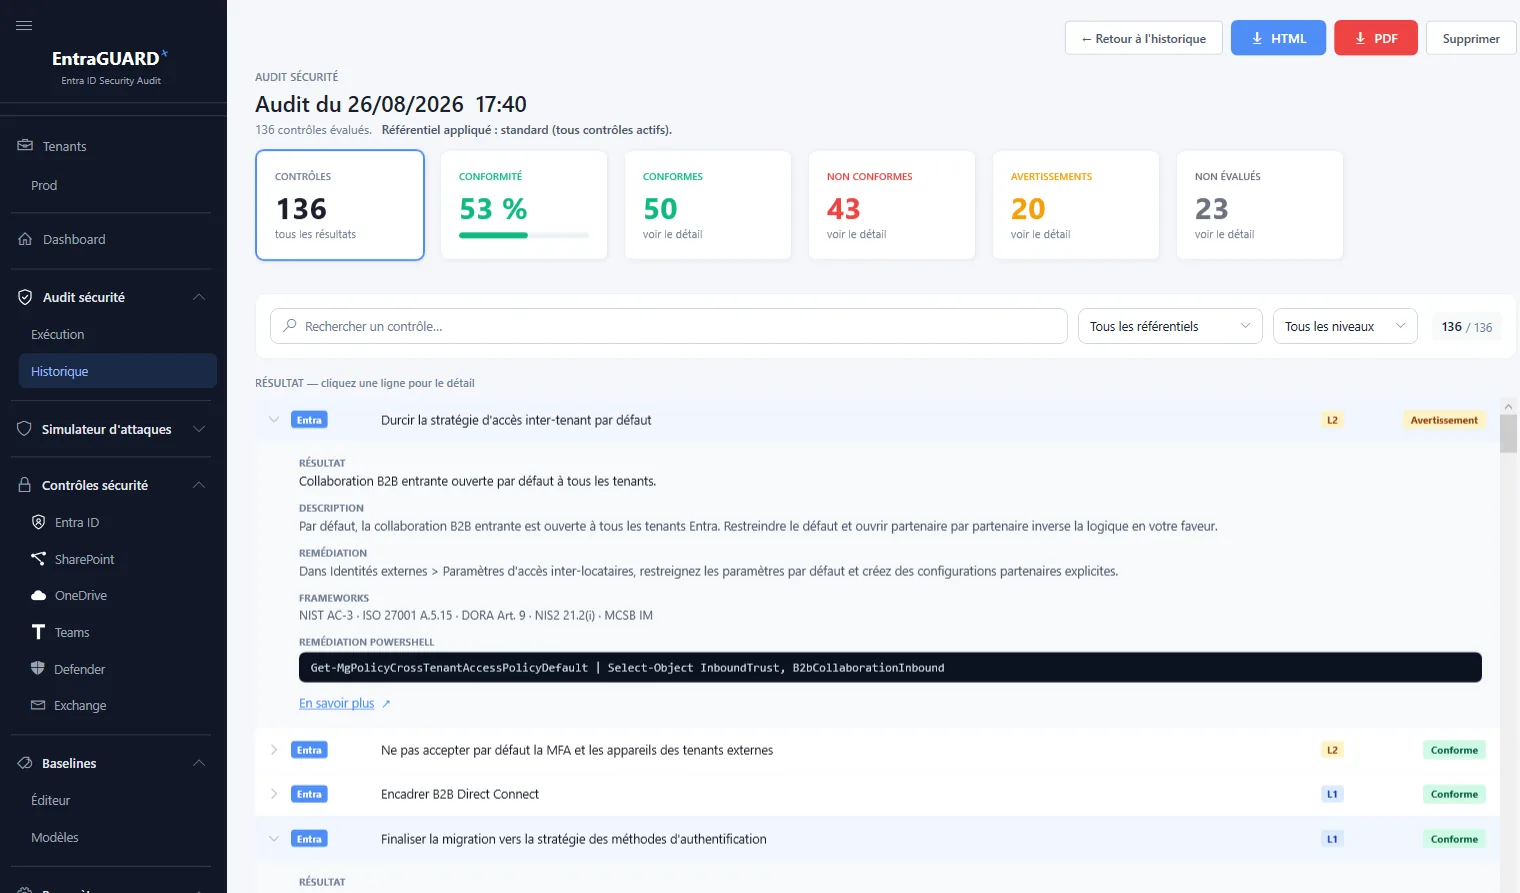
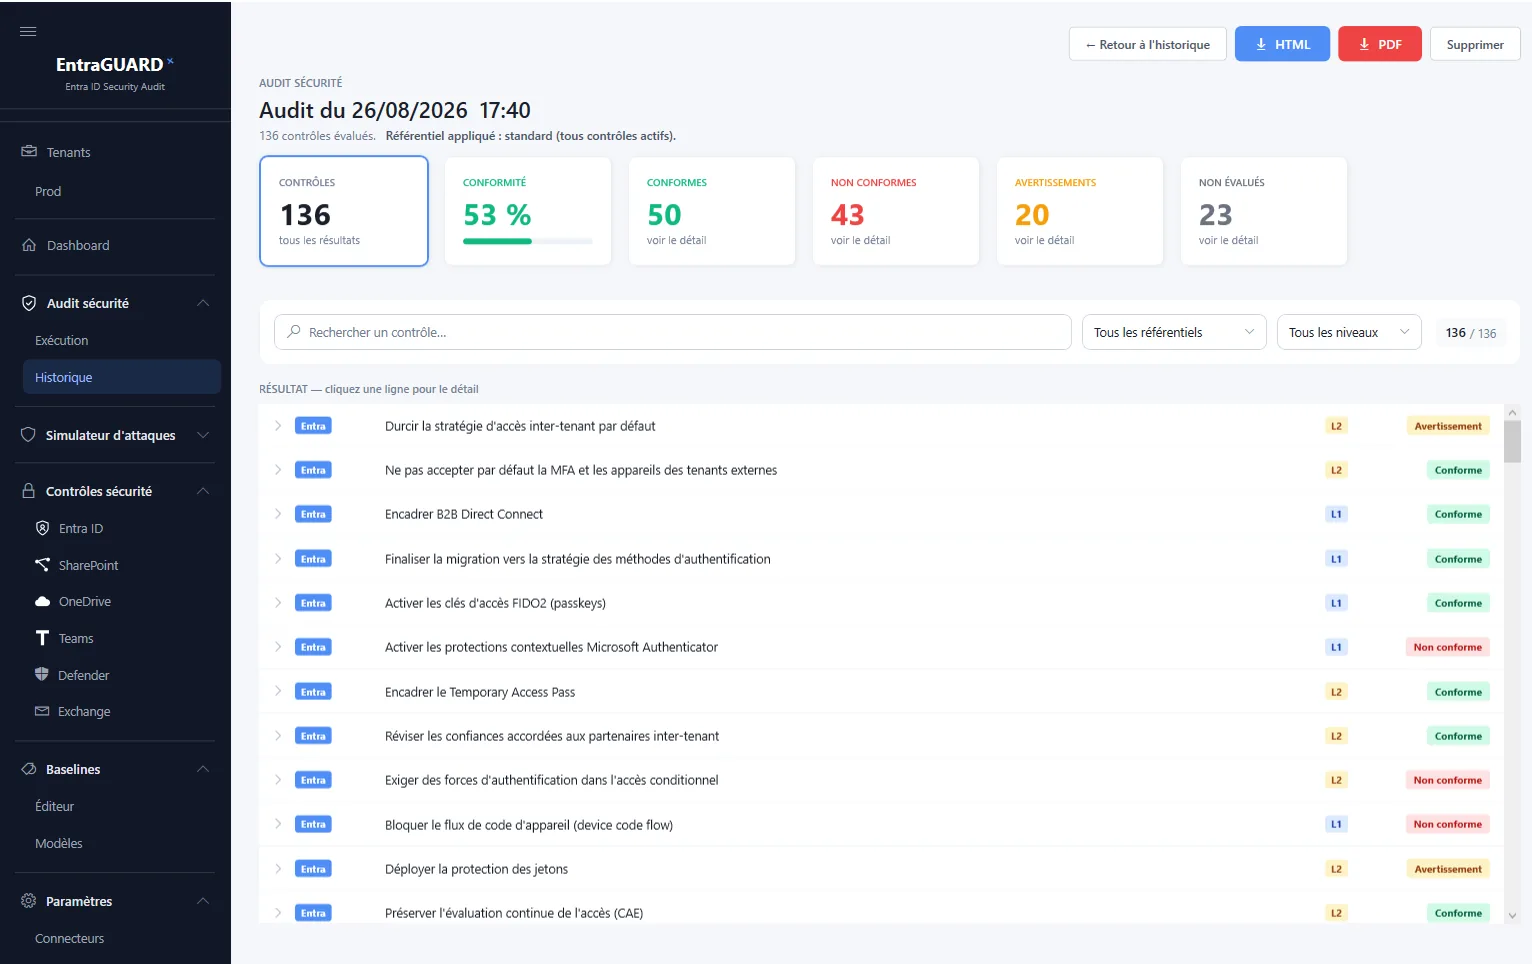
Audit detail: counters for controls, compliance, compliant, non-compliant and warnings, filters, HTML and PDF export, and an expanded control showing result, description, remediation and framework references

Then every control, one click deep

Five counters across the top, a search box and filters by referential and by level. Open a row and you get what an assessor has to write anyway: the observed state — "Microsoft Authenticator enabled (number matching enforced by Microsoft)" — what the control tests, the remediation as a portal path, and the references it satisfies: CIS Entra ID · NIST IA-2 · ISO 27001 A.8.5. Export is HTML or PDF, and the screen states that it covers the whole audit rather than the filtered view.

Audit history listing each run with its scope, score, counts and trend against the previous run

Every run is kept, with its scope

Date, number of controls evaluated, the services actually included, the score and the three counts — plus the movement against the previous run, already computed. A run over 19 controls sits next to one over 194 and is visibly not the same exercise, which is exactly what you want before you compare them.

Three outcomes

Compliant, non-compliant, or a judgment call

On that run, 82 of the 194 results are warnings — a setting that isn't a failure but that an assessor should look at, like certificate-based authentication being disabled. A pass/fail tool has to round every one of those in some direction; here they stay visible as what they are.

Trend

Movement without arithmetic

Each history entry shows how it moved against the run before it — stable, up two points, down thirteen. You know whether last month's remediation worked before opening anything, and the full comparison is one button away.

Export

The whole audit, not the filtered view

HTML and PDF from the results screen, and the app states plainly that the export covers the entire audit rather than whatever your current filter shows — a small thing that stops a client receiving an accidentally truncated report.

Performance

Speed is a setting, not luck.

Controls are evaluated in parallel. The right number at once depends on the workstation and on how much load the Microsoft APIs will tolerate — so instead of hard-coding a guess, the application exposes the setting and measures the correct value on the machine that will actually run the audits.

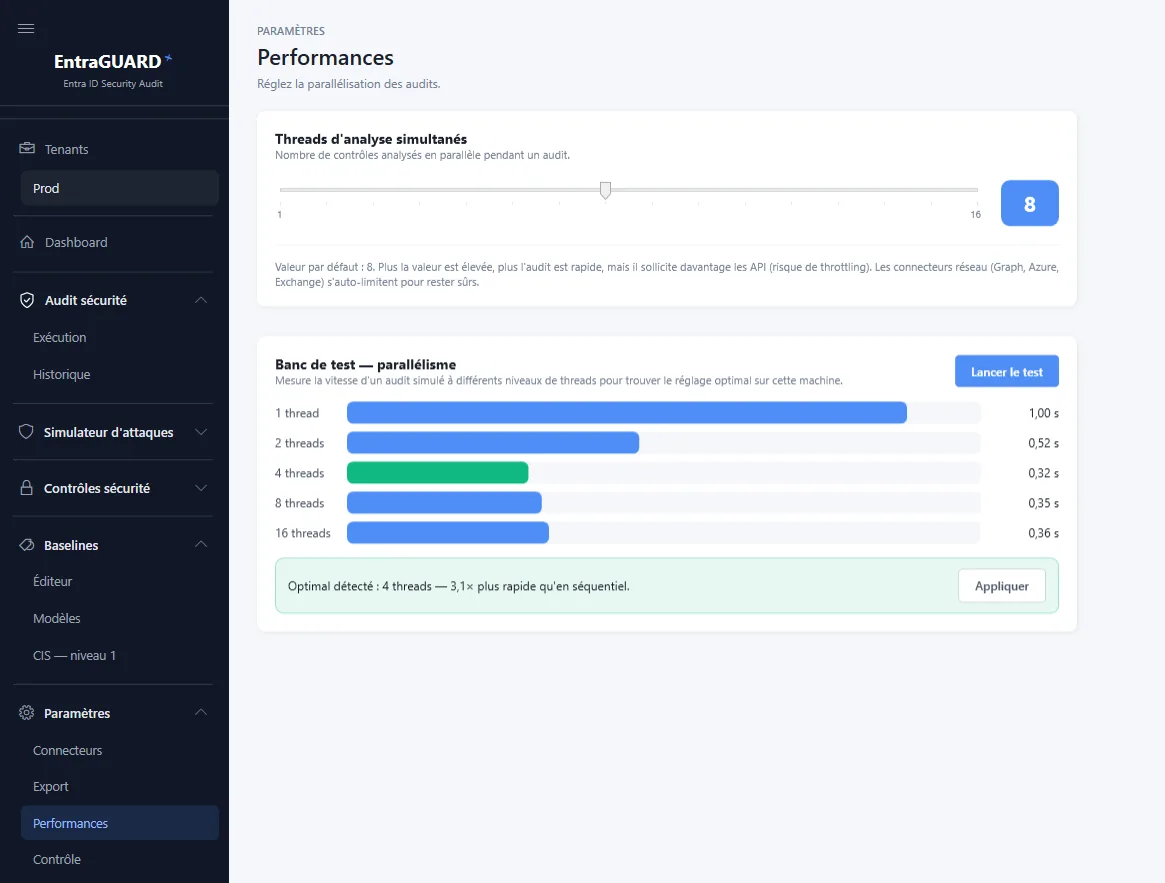
Performance settings: concurrent analysis thread slider and a parallelism benchmark comparing run times at 1, 2, 4, 8 and 16 threads
Settings › Performance — the thread slider and the on-device benchmark.
  1. Eight controls at a time, adjustable from one to sixteen

    The default suits most machines. Lower it on a constrained VM or a fragile tenant, raise it on a workstation with headroom — it takes effect on the next run, with nothing to reconfigure.

  2. Throttling is accounted for, not ignored

    The screen states the trade-off plainly: more threads means more load on the APIs and a real throttling risk. The network connectors — Graph, Exchange — self-limit regardless of where you put the slider, so a high setting degrades speed rather than breaking a client's tenant.

  3. A benchmark that runs on your hardware

    One click simulates an audit at each thread level and times it. On the machine in that screenshot: 0.99 s sequential, 0.34 s at eight threads — 2.9× faster — and slower again at sixteen. The curve is measured, not assumed, so the tool recommends eight instead of maxing the slider, and applies it for you.

This is the mechanism behind the sixteen-second run in the section above, and it is the kind of thing that decides whether an auditor uses a tool twice. Anyone who acquires the product gets the knob and the benchmark along with the rest of the source.

Test your exposure

Attack simulator

Beyond compliance, EntraGUARD replays an intruder's path: 35 read-only scenarios across three phases — initial access, persistence & escalation, configuration & exposure. Nothing is changed in the tenant; each scenario simply checks whether the path would succeed.

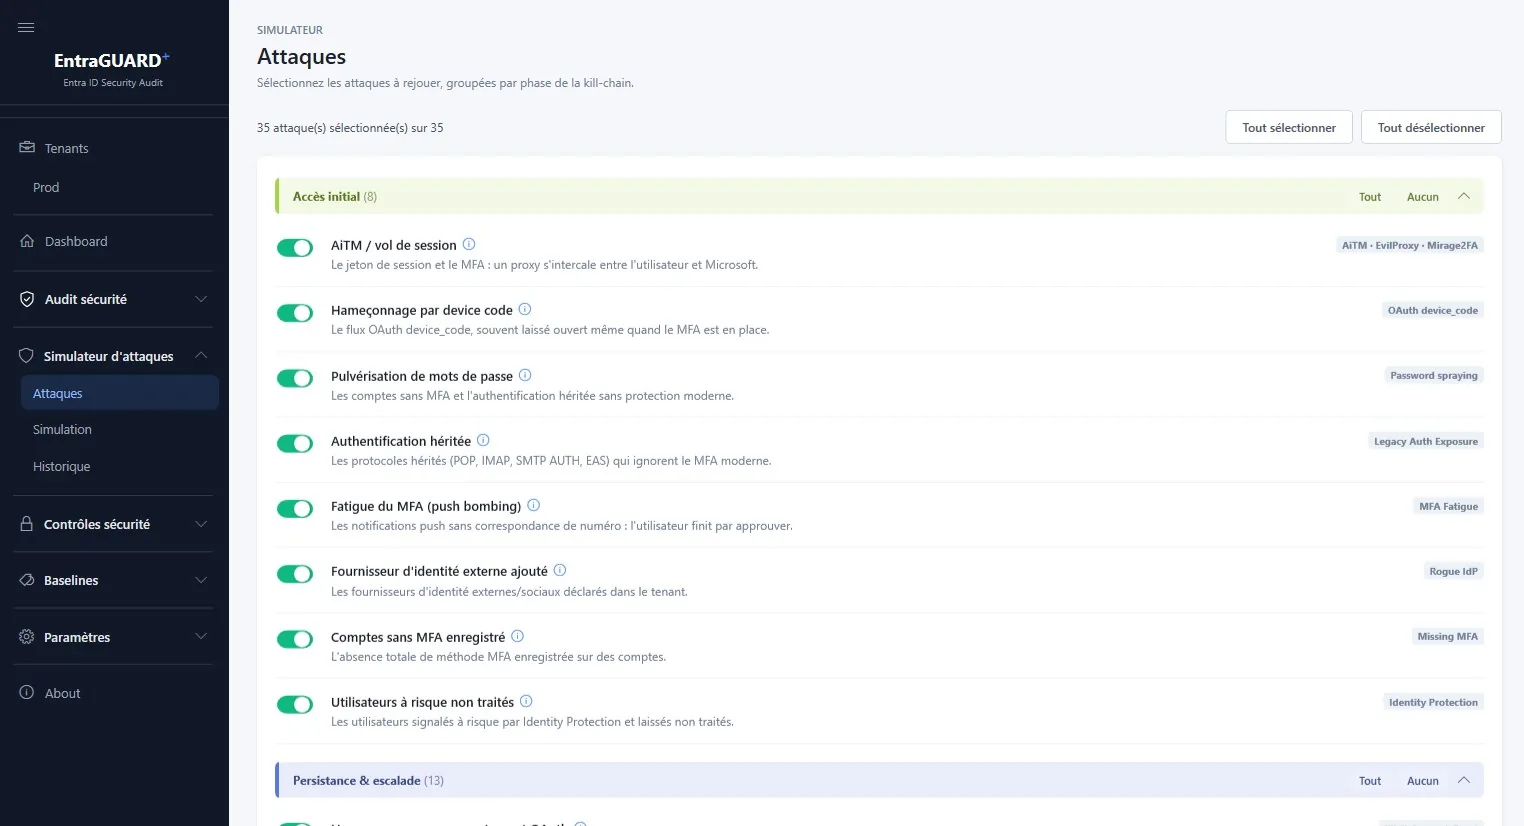
Attack scenario catalog: AiTM, device code, OAuth consent, password spraying, with per-scenario activation

35 scenarios, three phases

The catalog lists each real technique — AiTM, device-code phishing, illicit OAuth consent, password spraying, hidden admin… — individually switchable, with its phase and description.

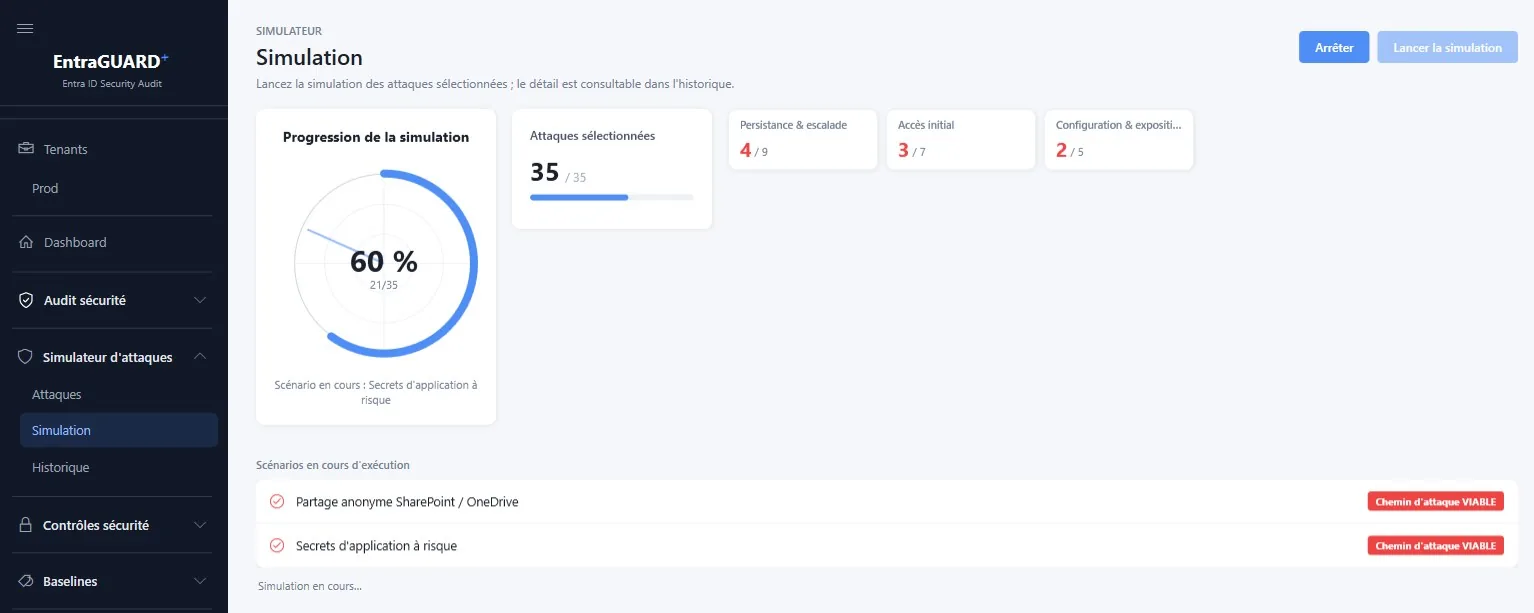
Simulation running with scenario progress

The simulation runs before your eyes

Each scenario tests its steps one after another — initiate the flow, observe sign-ins, escalate — and stops where your configuration blocks it. Everything is read-only.

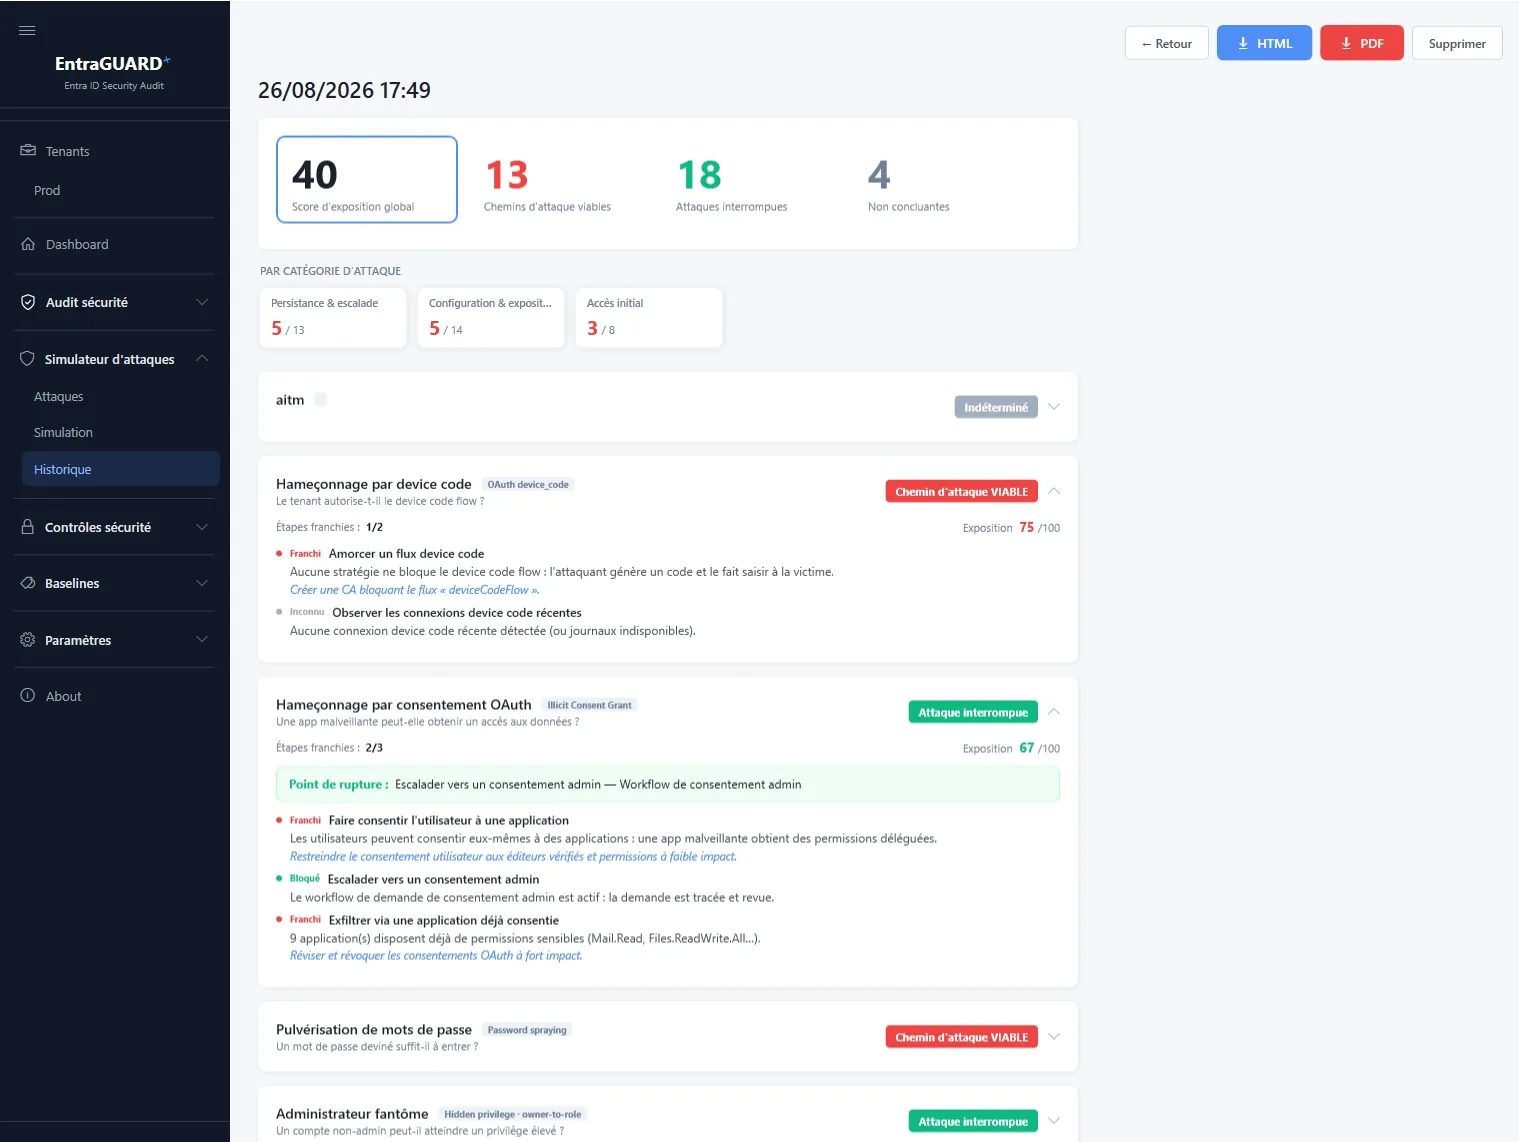
Results: global exposure score, viable attack paths, interrupted attacks, per-scenario detail with break point

An exposure score, viable paths

A global exposure score — 40/100 here — with the count of viable attack paths and interrupted attacks. Each expanded scenario shows the steps crossed, the break point that stopped the attack, and the remediation that cuts the path.

What you get

Four reports, four audiences.

The same audit produces the document each reader actually needs — from a one-page board summary to a line-by-line remediation plan an engineer can work through.

Executive summary

Cover page under your brand and the client's, overall posture, per-service breakdown, and the findings that matter to a board.

PDFHTMLXLSXCSVJSON

Detailed audit

Every control, its verdict, the objects concerned, and the reference it was tested against.

PDFHTMLXLSXCSVJSON

Framework compliance

The same results re-cut by each of the nineteen frameworks — CIS, NIST 800-53 and CSF, CMMC, FedRAMP, ISO 27001, NIS2, DORA and the rest — with the clause reference on every control.

PDFHTMLXLSXCSVJSON

Remediation plan

Failures ordered by weight, with the portal path and PowerShell command for each fix.

PDFHTMLXLSXCSVJSON

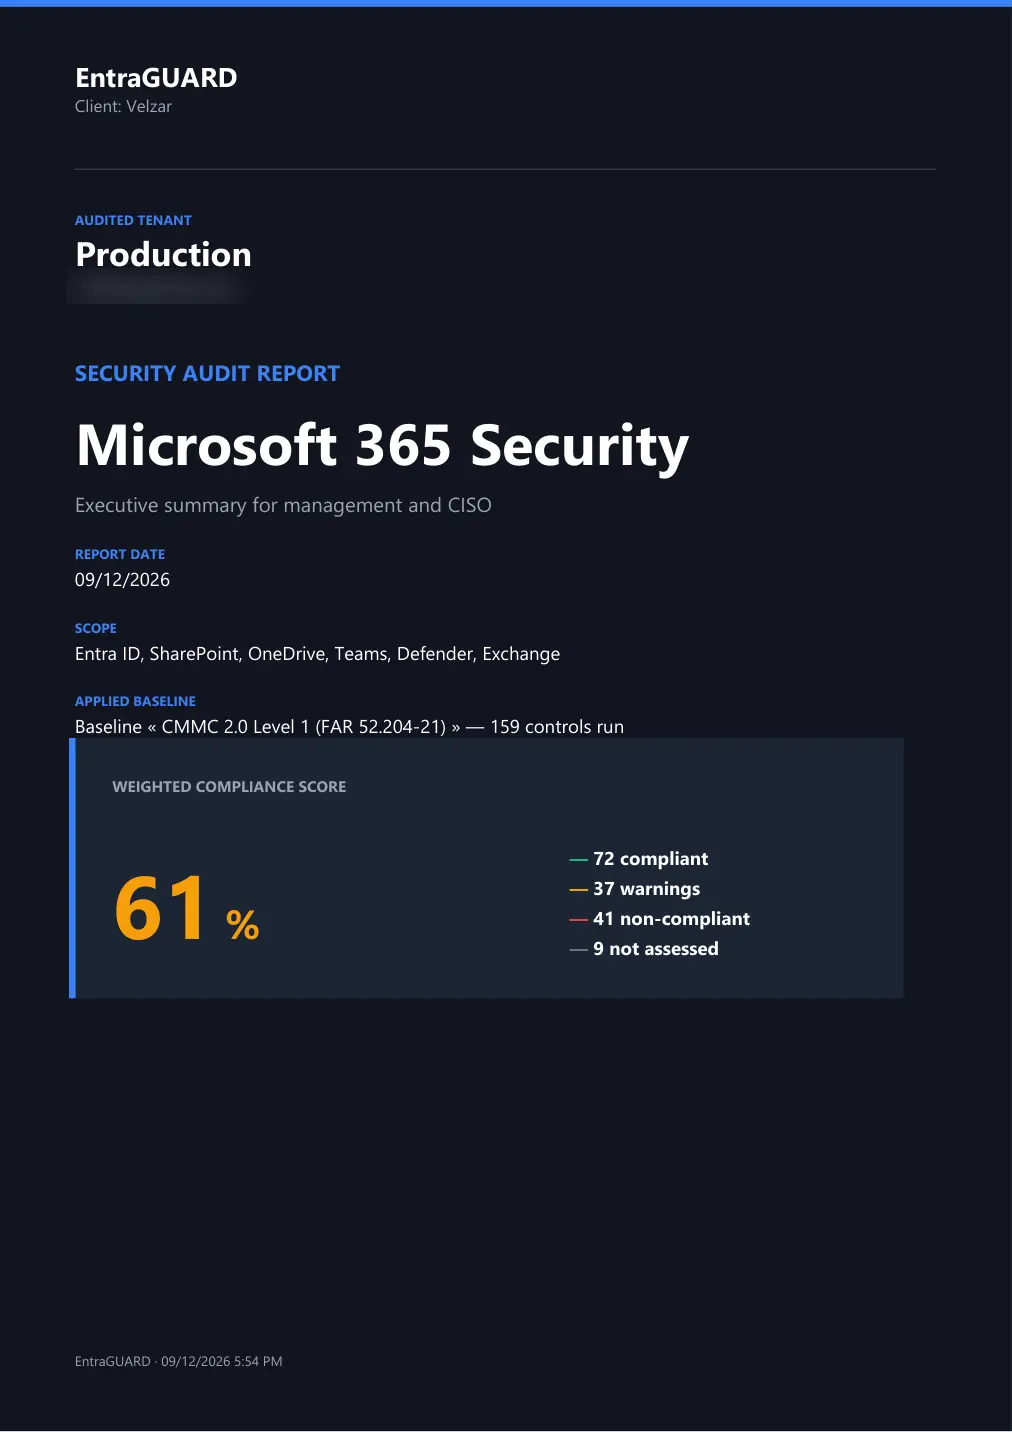
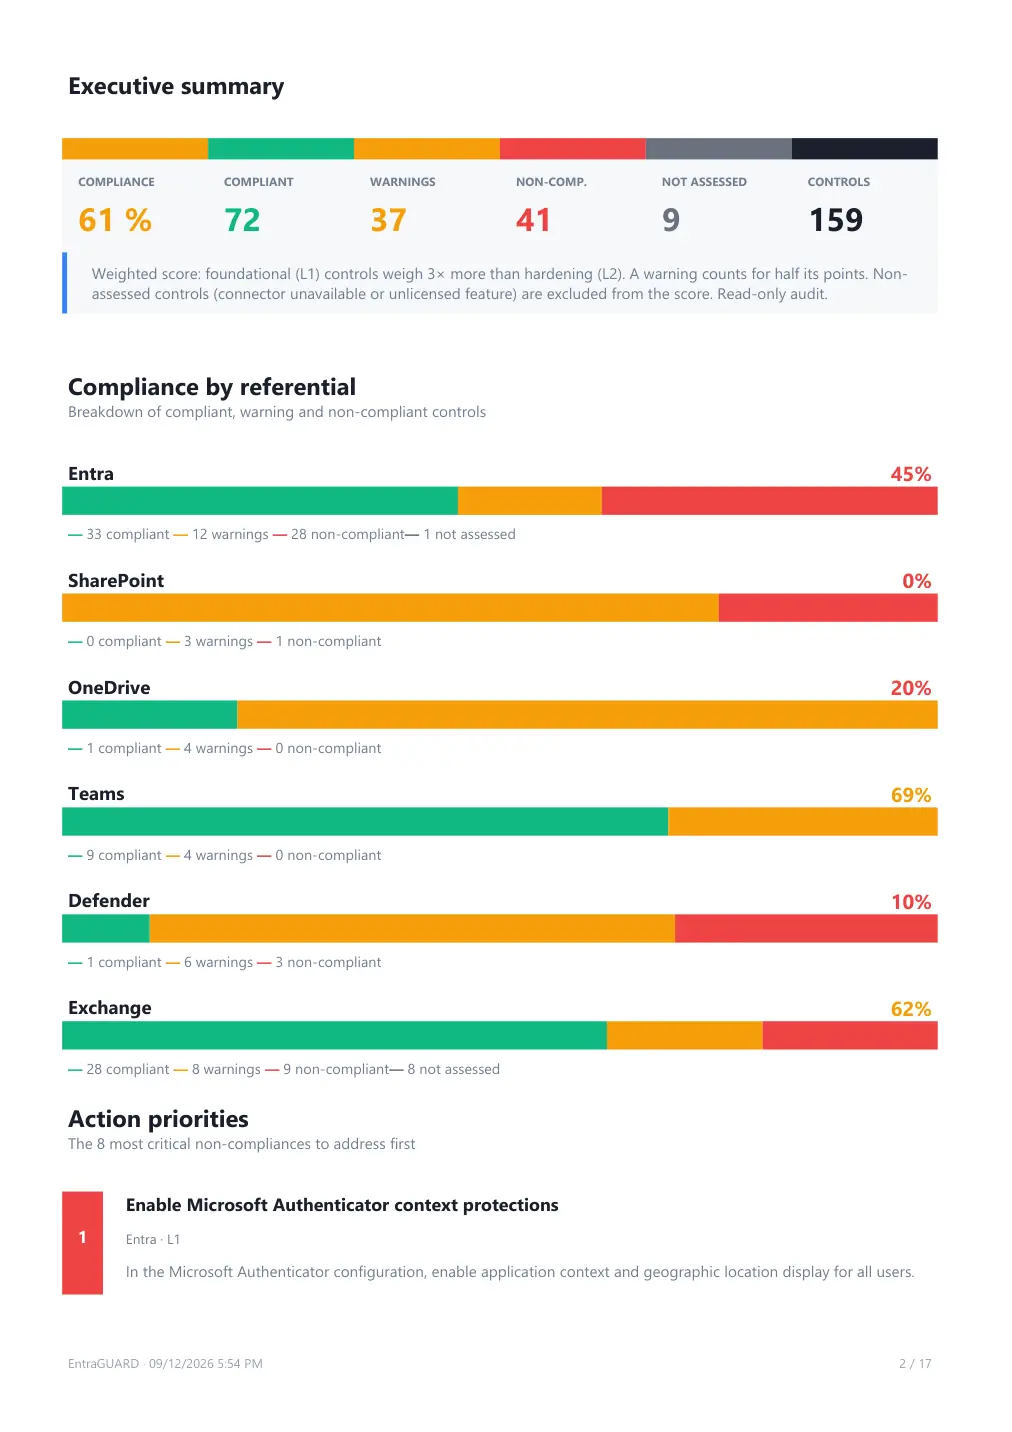
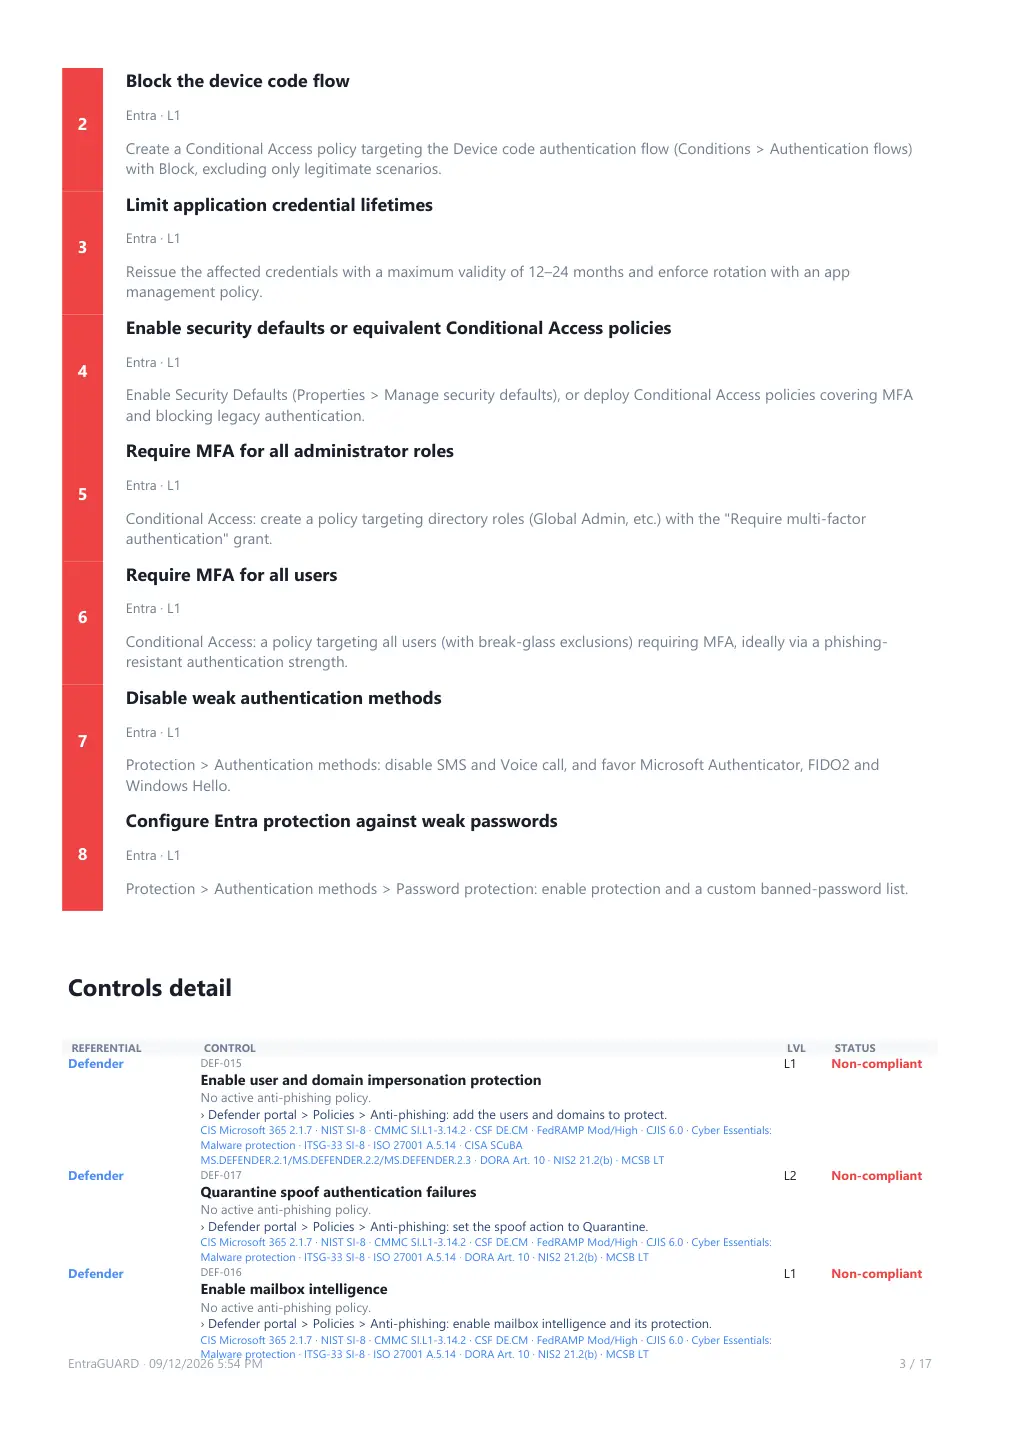
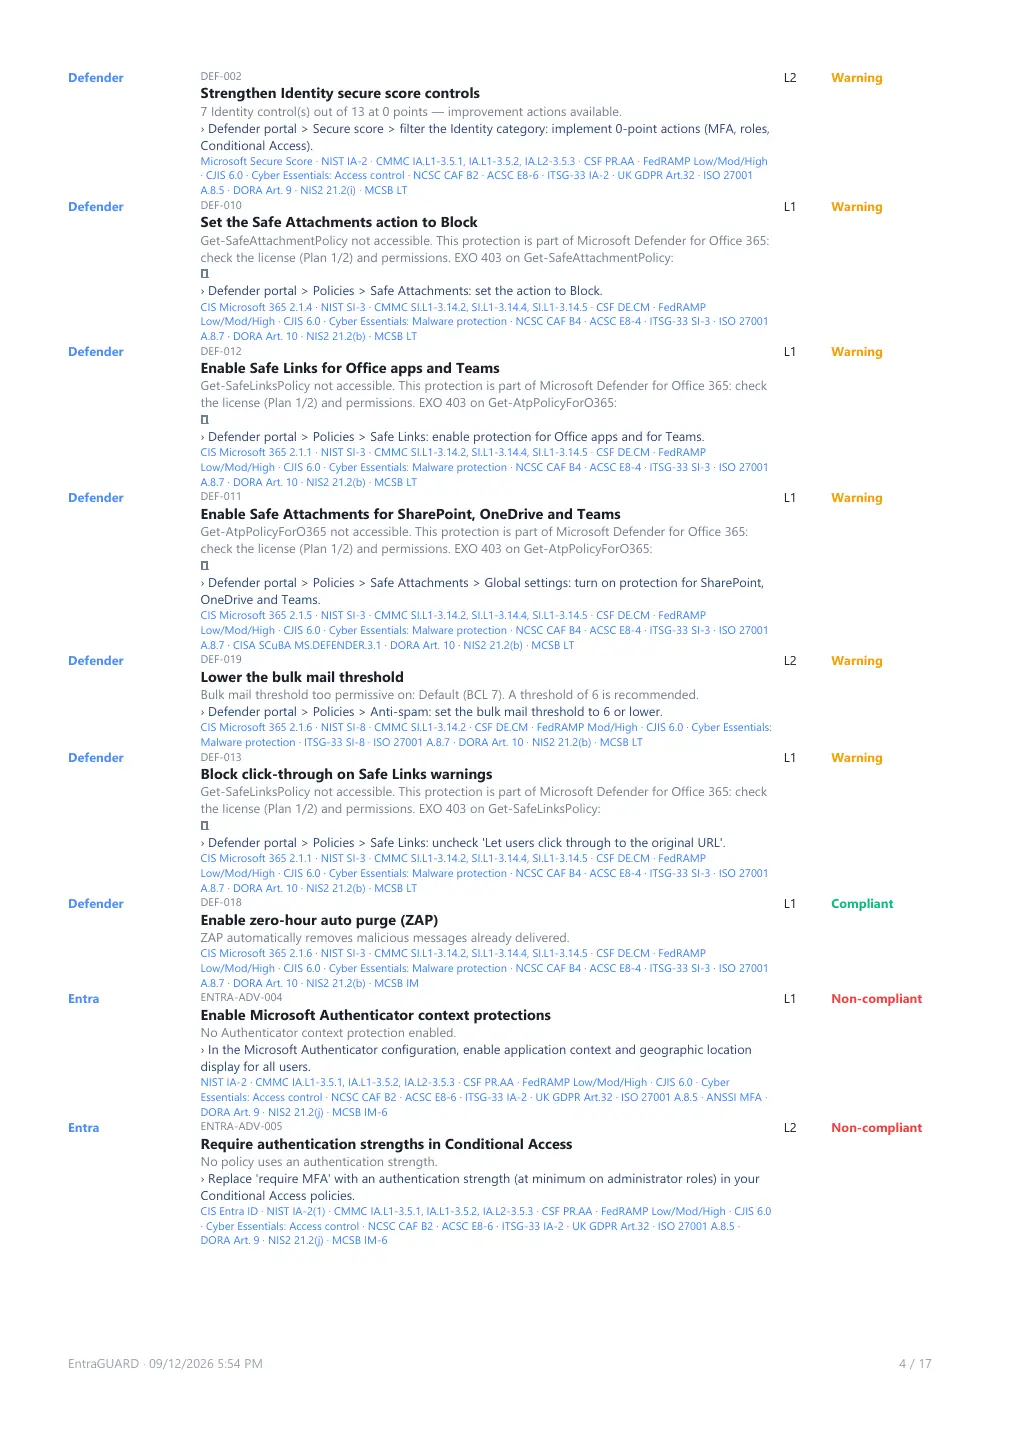
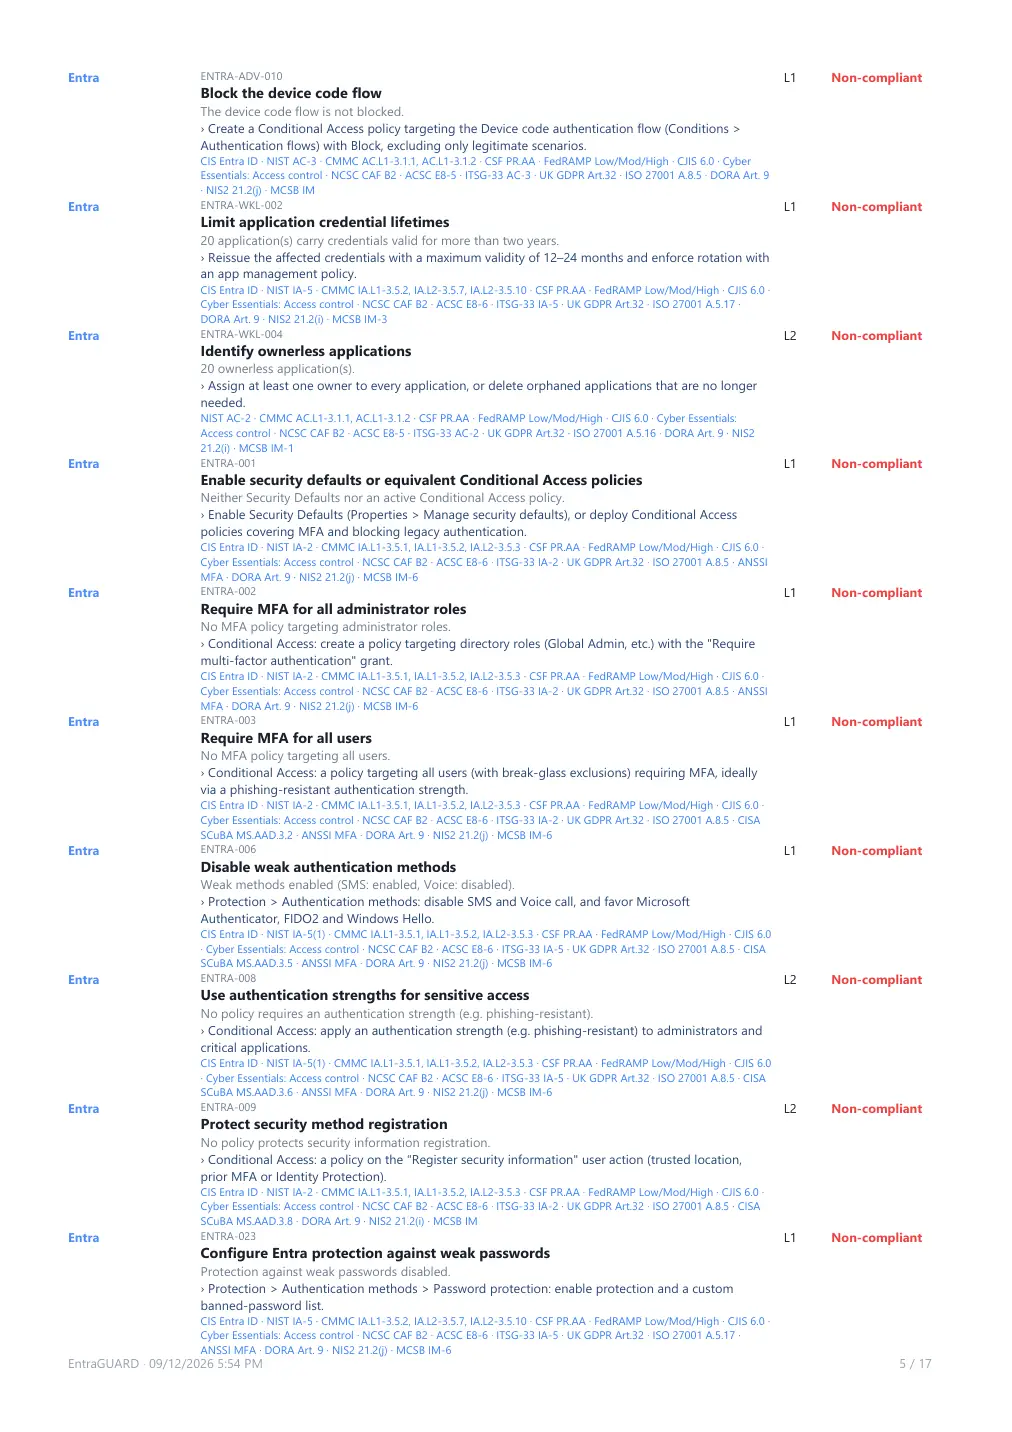
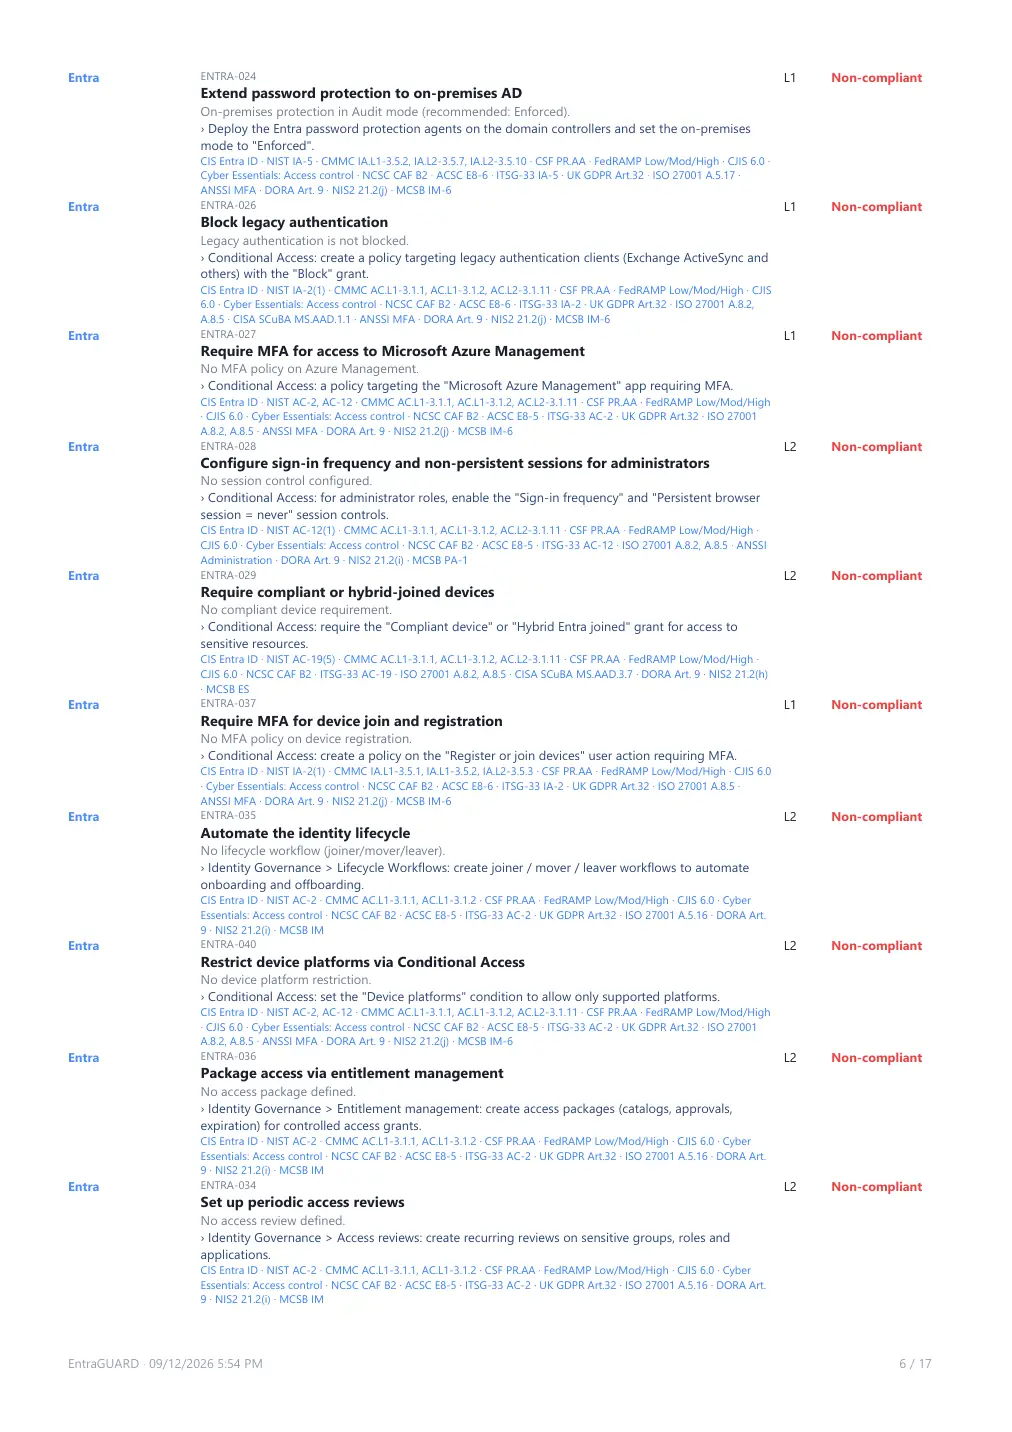
Executive summary — extract

The opening pages of a single run: weighted score, compliance per service, the action priorities, then the control-by-control detail with its verdicts and framework references.

6 of 17 pages159 controlsCMMC 2.0 Level 1

Download the sample (PDF, 1.1 MB)
Executive summary report, page 1 of 6 Executive summary report, page 2 of 6 Executive summary report, page 3 of 6 Executive summary report, page 4 of 6 Executive summary report, page 5 of 6 Executive summary report, page 6 of 6

Produced by EntraGUARD on a live tenant, under the auditor's own branding — a run of the CMMC 2.0 Level 1 baseline, 159 of the 318 controls. The audited domain is masked here. Click a page to enlarge it.

For auditors & assessors

Evidence, not opinion.

An assessment stands or falls on whether someone else can re-run it and reach the same conclusion. EntraGUARD was built around that constraint: every verdict carries the control it came from, the objects it looked at, the date it was taken and the requirement it answers in each of the nineteen frameworks it is mapped to.

318

implemented controls

19

frameworks cited per run

5

export formats

0

write permissions

Traceability

Every finding names its objects

A non-compliant control doesn't just say "fail". It lists the accounts, mailboxes, policies or resources that caused it — "20 applications carry credentials valid for more than two years" — timestamped and attributed to the tenant it was read from, which is the level of detail a working paper actually needs.

Reproducibility

Same baseline, same result

Scope is declared as a baseline — CMMC 2.0 Level 1, CIS Level 1, ISO 27001 Annex A.8, whichever the engagement calls for — and stored with the run. A second assessor applying the same baseline to the same tenant evaluates the same checks in the same order, and any difference is a real change in the environment.

Independence

Read-only, so it can't disturb what it measures

The tool holds no write permission, so running an audit never alters the environment under assessment and never competes with the client's own change process. The consent screen is the proof.

Framework view

Nineteen frameworks, on every control

CIS Benchmarks, NIST SP 800-53 and CSF 2.0, CMMC 2.0 / SP 800-171, FedRAMP, CJIS 6.0, CISA SCuBA, ISO 27001:2022, NIS2, DORA, ANSSI, UK GDPR Art. 32, Cyber Essentials, NCSC CAF, ACSC Essential Eight, ITSG-33, MCSB, MITRE ATT&CK and Microsoft Secure Score — each control carries its clause in every framework that covers it, so one run answers a certification file, a client questionnaire and a gap analysis at once.

Working papers

A control × framework matrix, not just PDF

Results export as PDF, HTML, XLSX, CSV and JSON, including the matrix a C3PAO, a SOC 2 auditor or a QSA asks for: one row per control, one column per framework, the mapped requirement identifier and the audit verdict in the cell. Nothing has to be retyped out of a report.

Honest scoring

Not assessed is a verdict of its own

A control the connector couldn't reach — an unlicensed feature, a permission denied — is reported as not assessed and excluded from the score rather than silently passed. Warnings count for half their weight, and an L1 failure costs three times an L2, so the percentage means something to the person signing under it.

Why now

The demand isn't a trend. It's a calendar.

Microsoft 365 and Entra ID are the identity layer for most organisations, credentials are how most intrusions now begin, and a run of regulations has turned “we take security seriously” into “show us the evidence.” None of those three reverses next year, which is what separates a market from a wave.

The install base

Everyone is a candidate

Entra ID is the front door to mail, files, Teams and increasingly to the cloud infrastructure behind them. Auditing identity means auditing the thing everything else depends on — and there is no vertical to specialise into, because the tenant is the same shape at a law firm, a hospital and a manufacturer.

The attack path

Intrusions start with a valid login

Incident reporting has converged on the same finding for several years running: attackers increasingly sign in rather than break in. That moves identity configuration out of IT hygiene and into the first question an insurer, a board or a forensic team asks after an incident — and the first one asked before it.

The obligation

Evidence, on a deadline

NIS2, DORA, ISO 27001:2022, SOC 2, CMMC, HIPAA. Different scopes and different regulators, one shared requirement: documented, repeatable proof that access controls are configured the way you say they are. A screenshot pasted into a Word document stopped being an answer.

The bottleneck

Demand is not the constraint

The organisations being asked mostly cannot answer for themselves, so they turn to their IT or security team — who answer by hand, in a spreadsheet, over two days per tenant. What limits this market is not appetite. It is the number of people who can produce the evidence, which is exactly what a tool changes.

NIS2EU Directive 2022/2555

Member states had to transpose it by October 2024; national enforcement has been ramping since. It pulls in far more mid-sized entities than the directive it replaced, and requires risk management measures to be demonstrable rather than declared.

DORAEU Regulation 2022/2554

Applicable since January 2025 to EU financial entities and, critically, to their ICT service providers. Access control and authentication sit squarely inside the resilience requirements.

ISO 27001:2022Annex A.5 and A.8

Certificates issued against the 2013 version had to migrate by October 2025. The 2022 Annex A puts configuration, access management and logging explicitly in scope — the exact ground a tenant audit covers.

CMMCUS Department of Defense

Phased into defense contracts from 2025, flowing down the supply chain to companies with no security team at all. Access control and identification and authentication account for the largest share of the requirements.

SOC 2 · HIPAAongoing, and tightening

Neither is new, but the evidence bar keeps rising: anyone selling software to a US enterprise is asked for CC6 and CC7 evidence, and any organisation touching health data is asked for its technical safeguards in writing.

Deliberately absent from this section: a market-size forecast. Anyone can buy one, nobody can verify it, and every line above can be checked against a published text instead. The point is not that the market is large — it is that the obligations have dates on them, and the people being asked still answer by hand.

Questions we get

Before you commit.

Does it audit Azure AD?

Azure AD is Microsoft Entra ID — Microsoft renamed it in 2023, the service is the same one. EntraGUARD audits it under its current name, together with Exchange Online, SharePoint, OneDrive, Teams, Defender, Purview and Intune, so an Azure AD security audit and an Entra ID security audit are the same run here.

Does it need Global Administrator?

No. The audit runs on read-only Microsoft Graph permissions. A Global Administrator is only needed once, to consent to the application registration — the same consent any read-only tool requires. After that, the audit account holds no privileged role.

How many tenants does it cover?

It depends on the tier: one tenant on Starter, three on Business and Enterprise, five on Enterprise+, ten on Corporate, and an unlimited number on the MSP tier. Any tier can take extra tenants at $149 a year each. Each client company is managed side by side, with its own connectors, history and branding.

Exactly which permissions are we granting?

Read-only application scopes on Microsoft Graph — Directory.Read.All, Policy.Read.All, RoleManagement.Read.Directory, Reports.Read.All, AuditLog.Read.All, DeviceManagementConfiguration.Read.All and DeviceManagementManagedDevices.Read.All (Intune), SharePointTenantSettings.Read.All, TeamworkAppSettings.Read.All, the SecurityAlert / SecurityEvents / SecurityIncident read scopes and a few more — plus Exchange.ManageAsApp for Exchange Online. No write scope is requested anywhere; the exact set is shown on your client's consent screen, which they can review before granting access.

Does anything leave our network?

Only the API calls to Microsoft, made from your workstation. There is no vendor backend, no analytics, and no upload of findings. Reports are files on your disk until you choose to send them.

Can we add our own controls?

Yes. The catalog loads from control packs, and you can import additional packs alongside the official ones. Custom checks can be defined declaratively against Graph or REST connectors.

How long does an audit take to run?

Several minutes, depending on the size of your tenant and its content. Checks are direct API reads run in parallel; the duration depends on the volume of objects to read. On an engagement, most of the time goes into consenting the connectors and reading the findings.

Does running controls in parallel risk throttling a client's tenant?

No. The connectors that talk to Graph and Exchange self-limit whatever you set the thread count to, so the worst case of an over-ambitious setting is a slower audit rather than a throttled tenant. The default is eight concurrent controls, adjustable from one to sixteen, and a built-in benchmark measures the optimum on your own machine.

Can we see it working before buying?

Yes — a demo version can be sent to you on request.

Is the source code included?

No. The standard offer is the application as a ready-to-run product, with its control catalog, framework mappings, report templates and technical documentation. Source code is not part of the package — it can be provided only under a separate prior agreement.

Can we resell it to our own clients?

Auditing your clients' tenants and billing them for the engagement is exactly what the MSP / Partner tier is for, and every tier lets you deliver the reports under your own brand. What is not permitted is reselling or redistributing the application itself, and that restriction is written into the license agreement.

Is support included?

Yes, by email, for the whole license period — together with product updates and every new control or attack pack released while your license runs.

Are you open to investment or an acquisition?

Yes, and to structures short of a full sale — an equity stake, a funded roadmap, or exclusive distribution. Financials, architecture documentation and a code walkthrough are available under NDA. Ask through the form and say which structure interests you.

Contact